Compyl

GRC

2027 Compliance Deadline Calendar: Security, Privacy & AI Dates
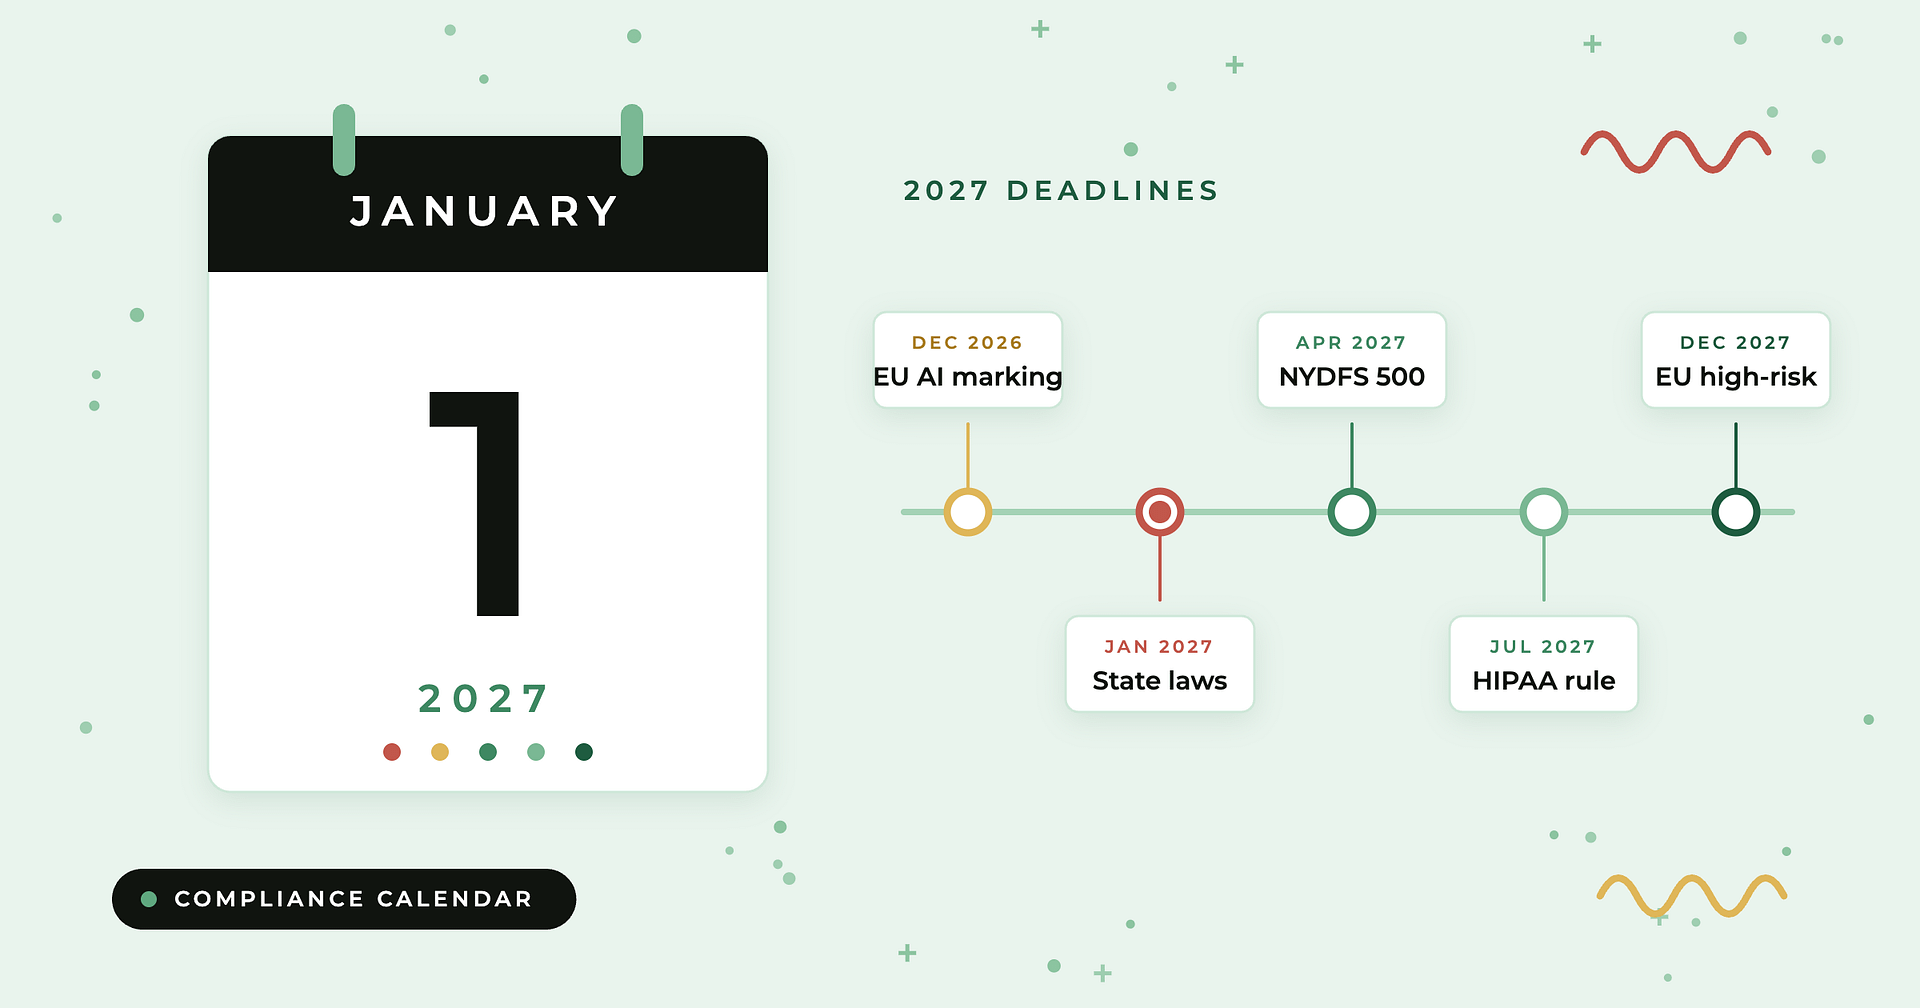
Compyl blog: 2027 compliance deadline calendar — a January 1, 2027 calendar page beside a timeline of key deadlines

A living calendar of every verified security, privacy and AI compliance deadline mid-market teams face from Q4 2026 through 2028, including the EU AI Act and HIPAA dates that moved in 2026.
Best Trust Center Software in 2026: 11 Tools Compared

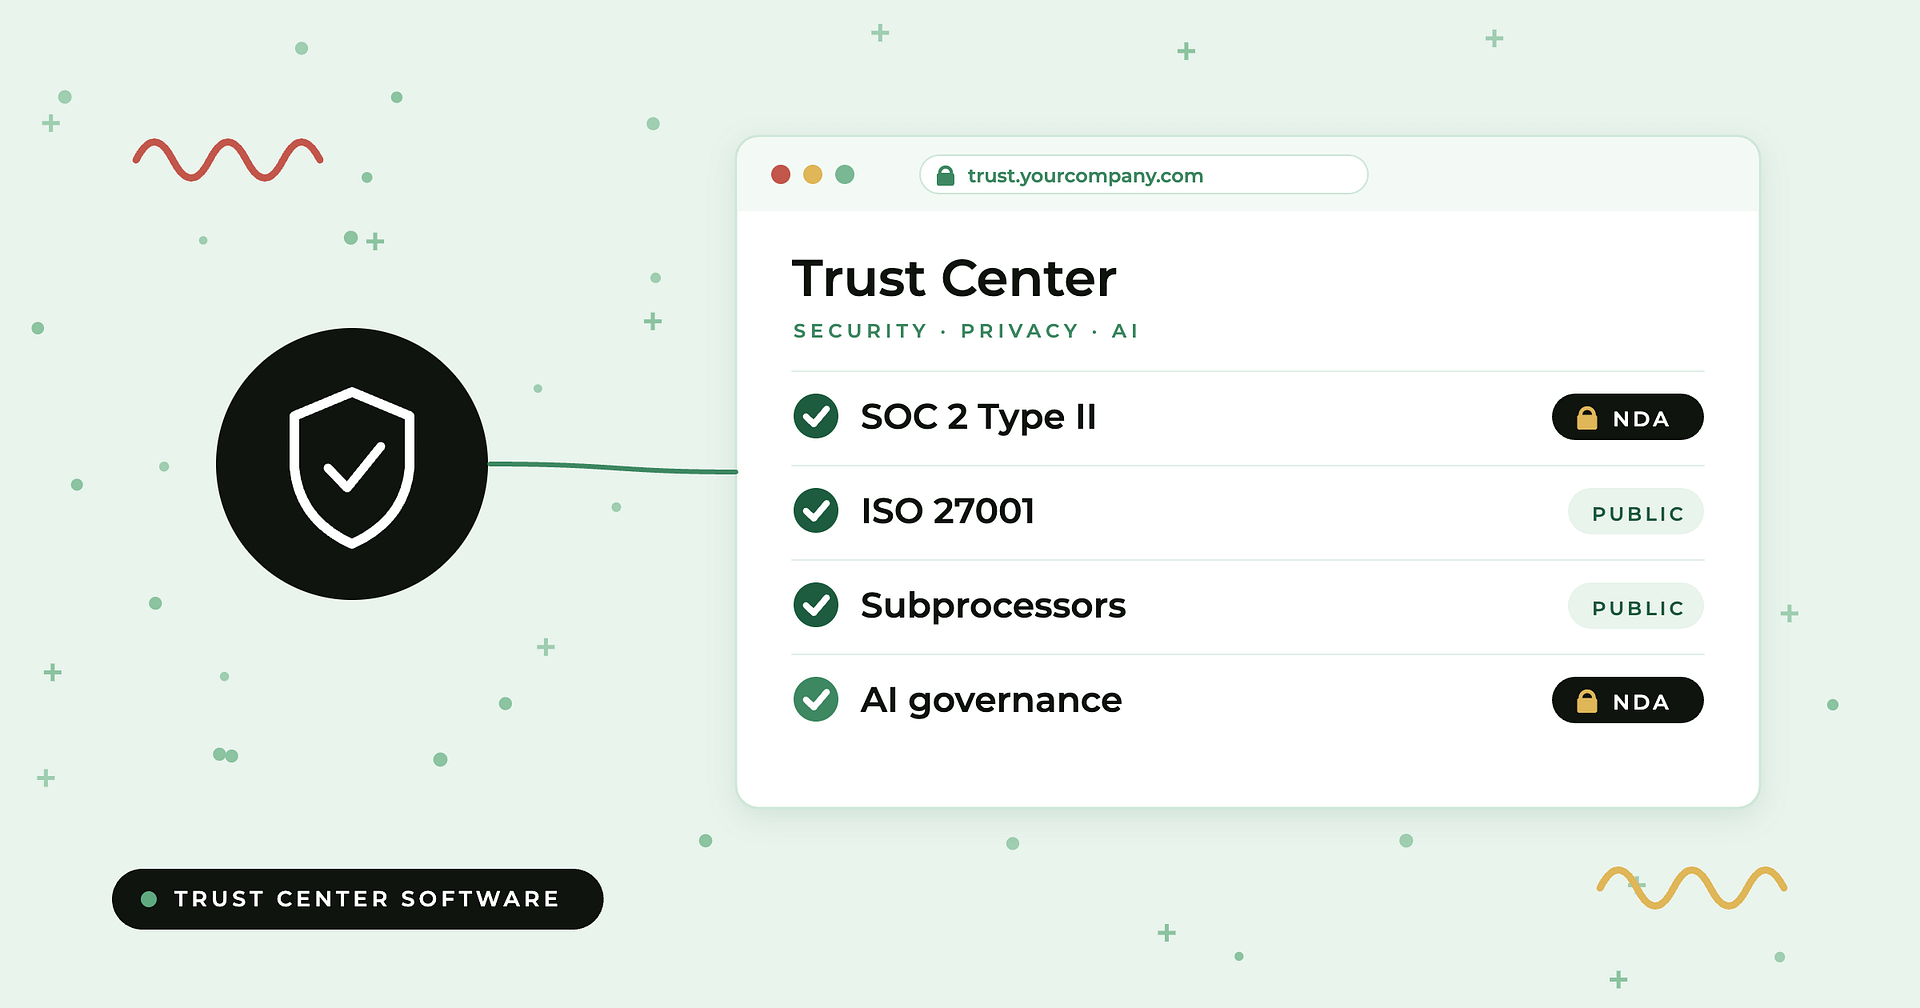
Compyl blog: Best trust center software in 2026 — a trust center portal window listing SOC 2, ISO 27001, subprocessors and AI governance with public and NDA access

The best trust center software in 2026, grouped by category: GRC platforms with a built-in trust center, compliance-automation tools, and standalone security review tools.

Best GRC Software for Mid-Market Companies in 2026

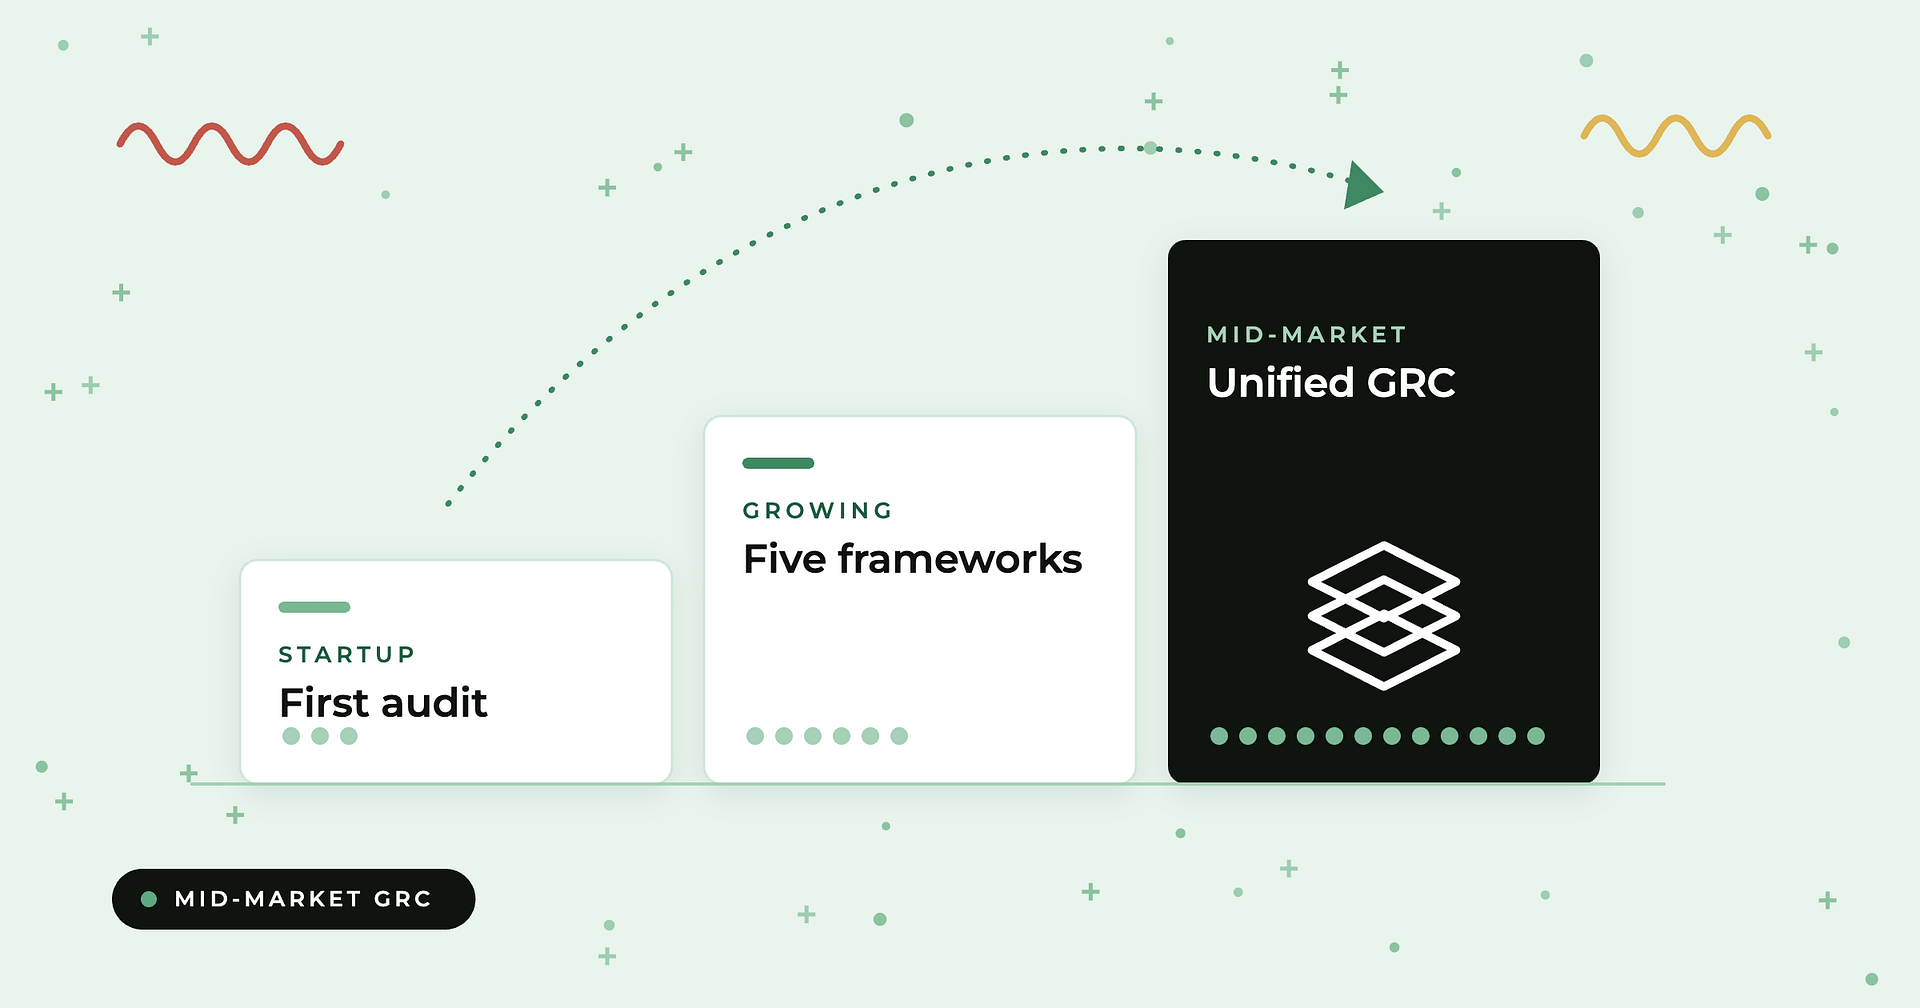
Compyl blog: Best GRC software for mid-market companies — three ascending stage cards from first audit to unified GRC

Which GRC software fits a 200–1,000-employee company depends on what is breaking first. We group the leading platforms by stage and need, with a decision table and the questions to ask before buying.

How to Evaluate an Integrated GRC Platform for Multi-Framework Compliance and a Unified Risk View

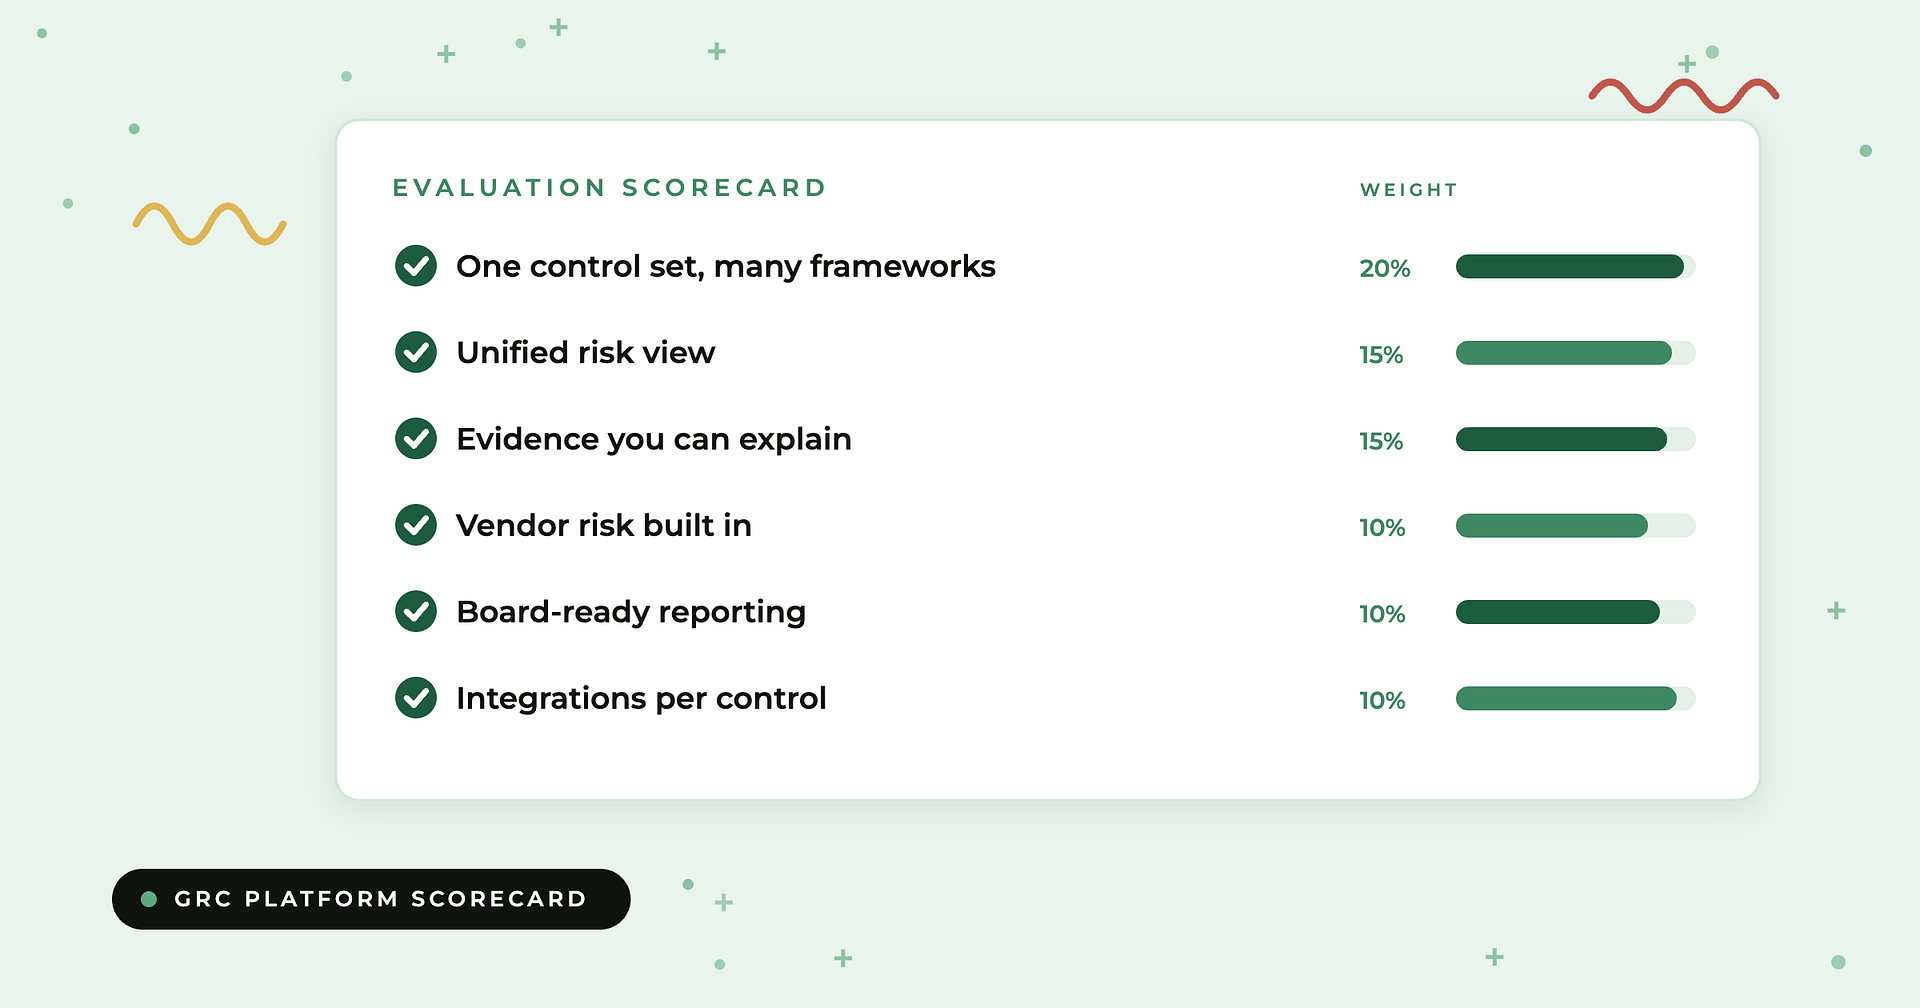
Compyl blog: How to evaluate an integrated GRC platform — a weighted evaluation scorecard of six criteria

A buyer’s guide for mid-sized and enterprise teams: the eight criteria that separate an integrated GRC platform from a compliance tool, a weighted scorecard, and the questions to ask vendors.

How to Replace Compliance Spreadsheets with a GRC Platform: A Phased Migration Plan

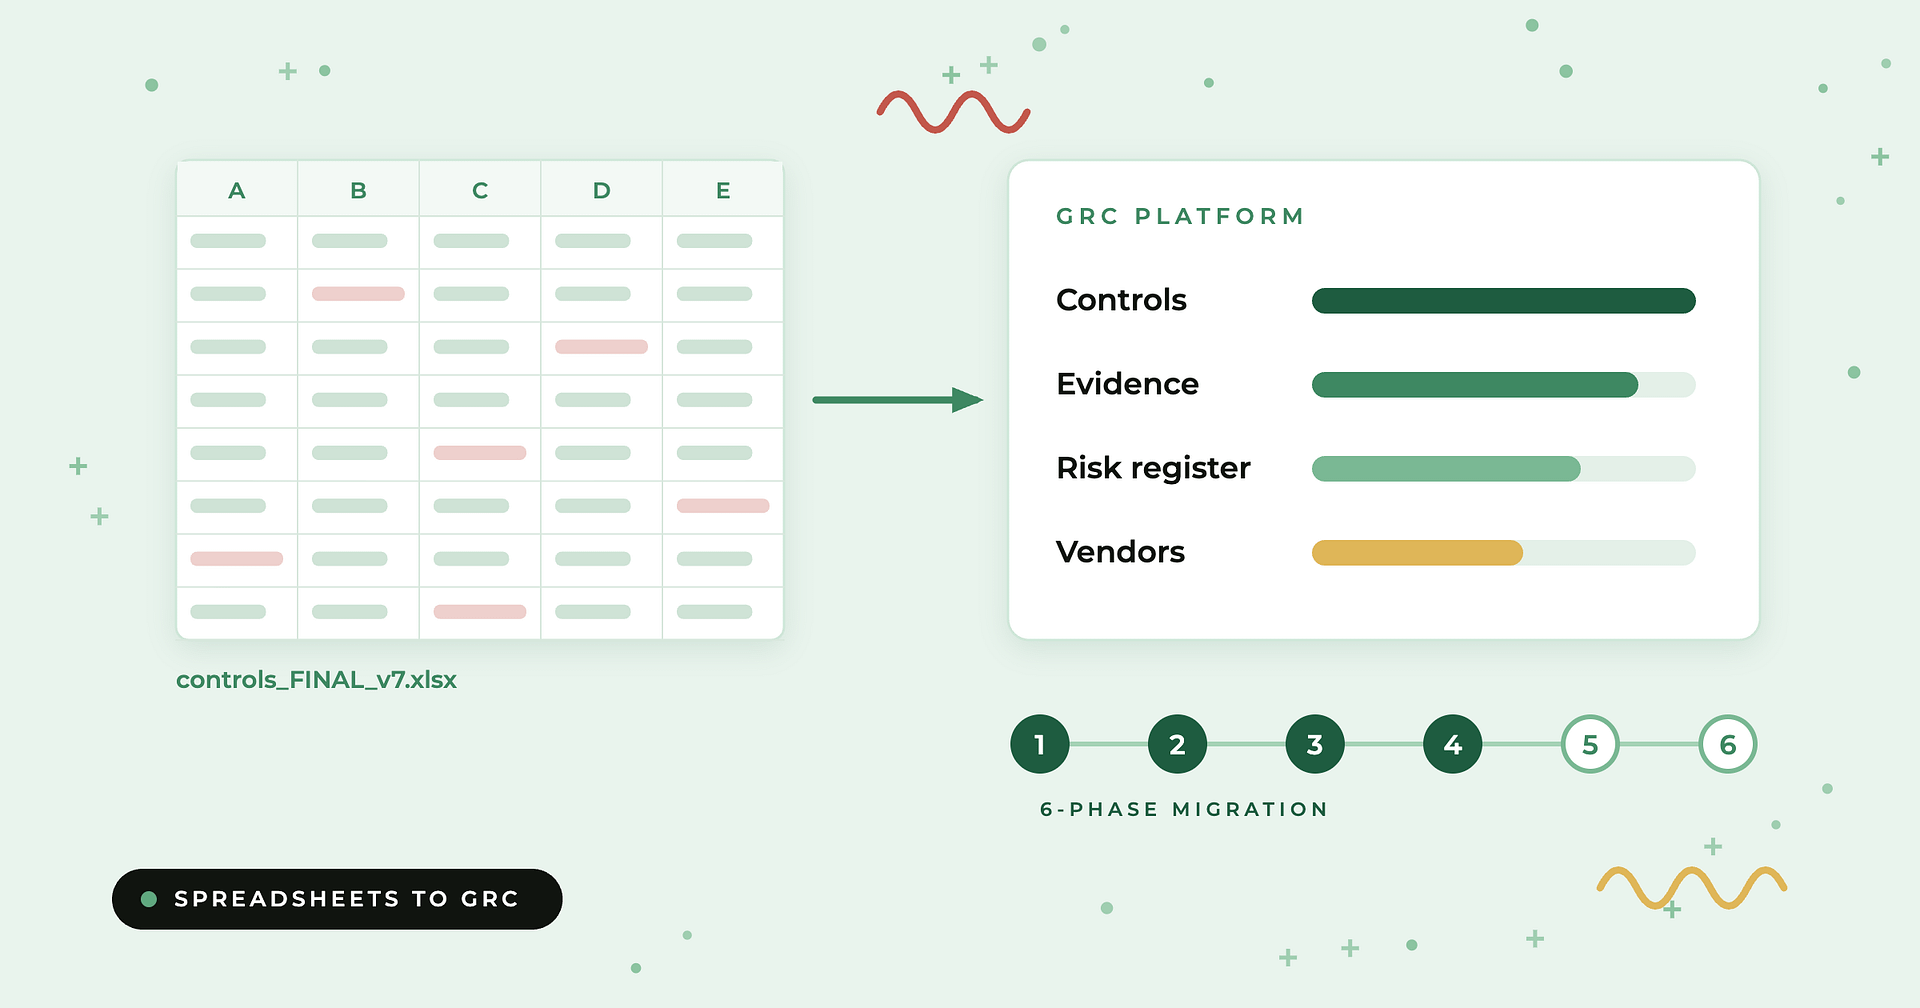
Compyl blog: Replace compliance spreadsheets with a GRC platform — a spreadsheet becoming a GRC platform view with a six-phase migration track

A six-phase plan for mid-market and enterprise teams moving their controls, evidence, risk register and vendor tracking out of spreadsheets and into an automated GRC platform.

GRC Challenges Mid-Market Technology Companies Face in 2026 (and How to Solve Them)

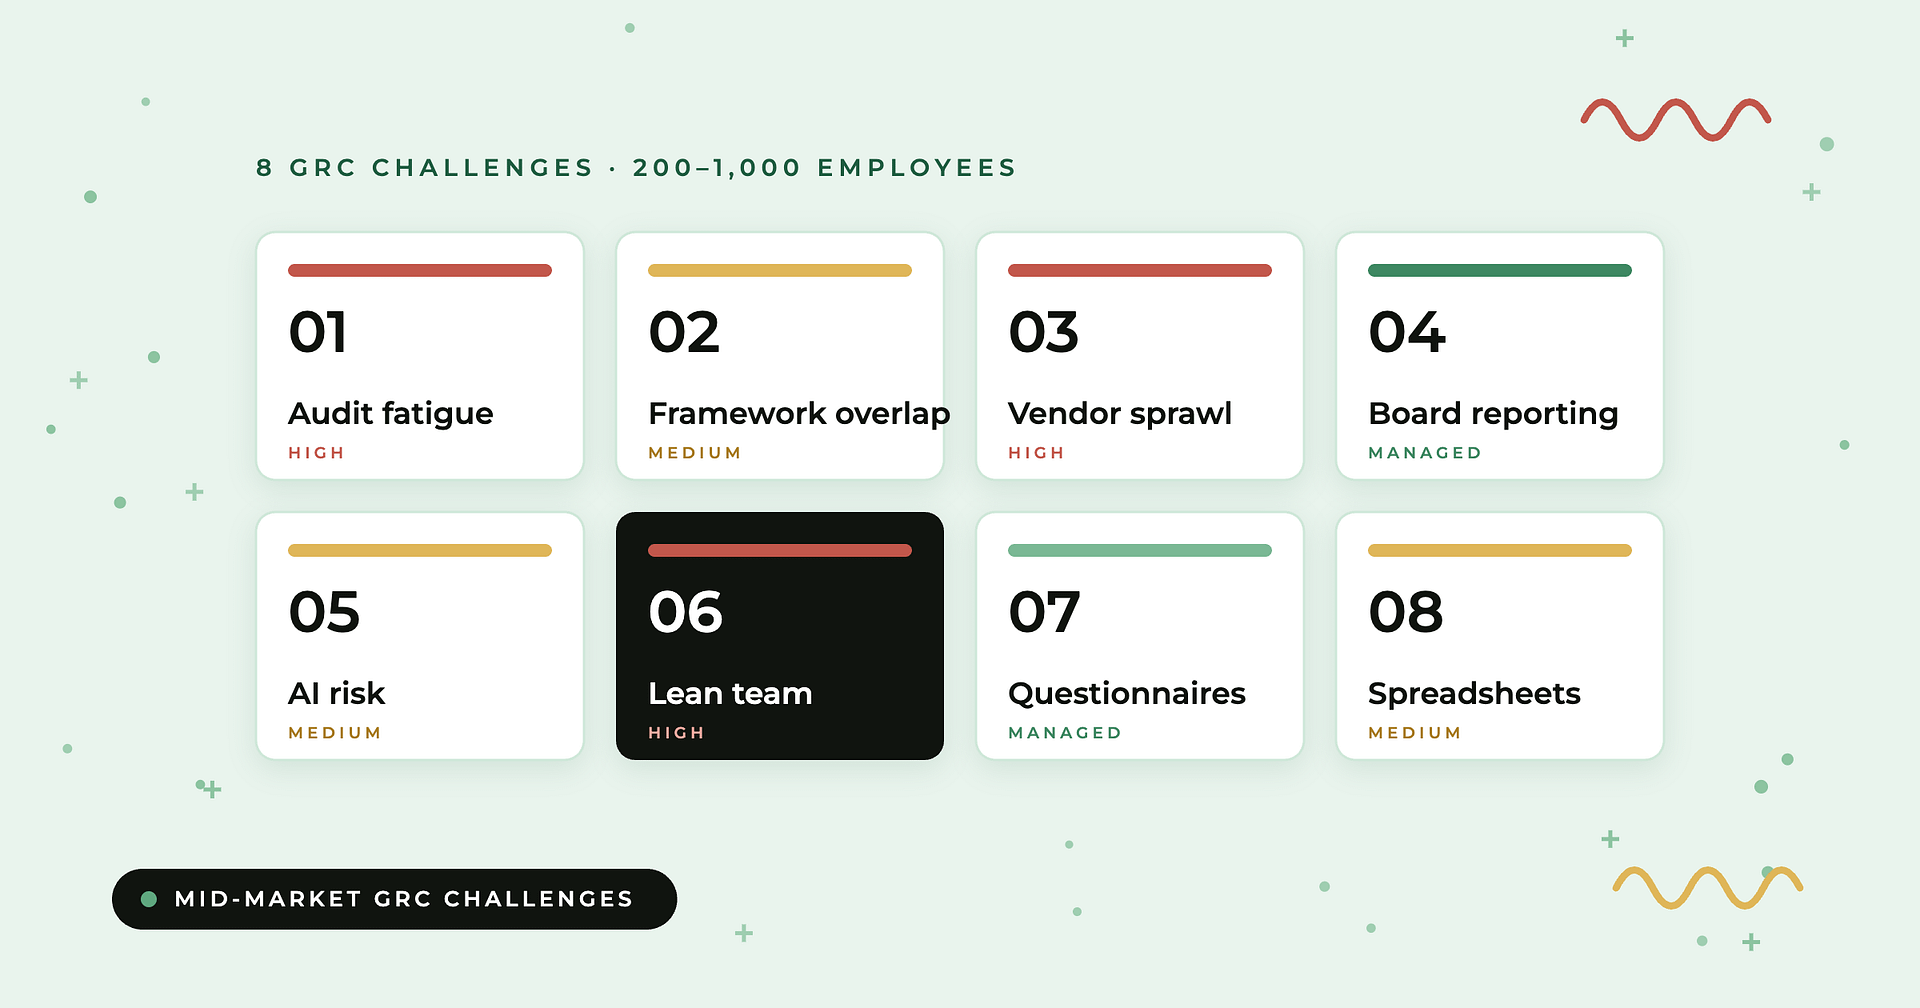
Compyl blog: GRC challenges for mid-market technology companies — eight numbered challenge tiles rated by severity

The eight governance, risk and compliance problems that hit technology companies between 200 and 1,000 employees, and what the teams that solve them do differently.

7 Signs You’ve Outgrown Vanta or Drata (and What to Move To)

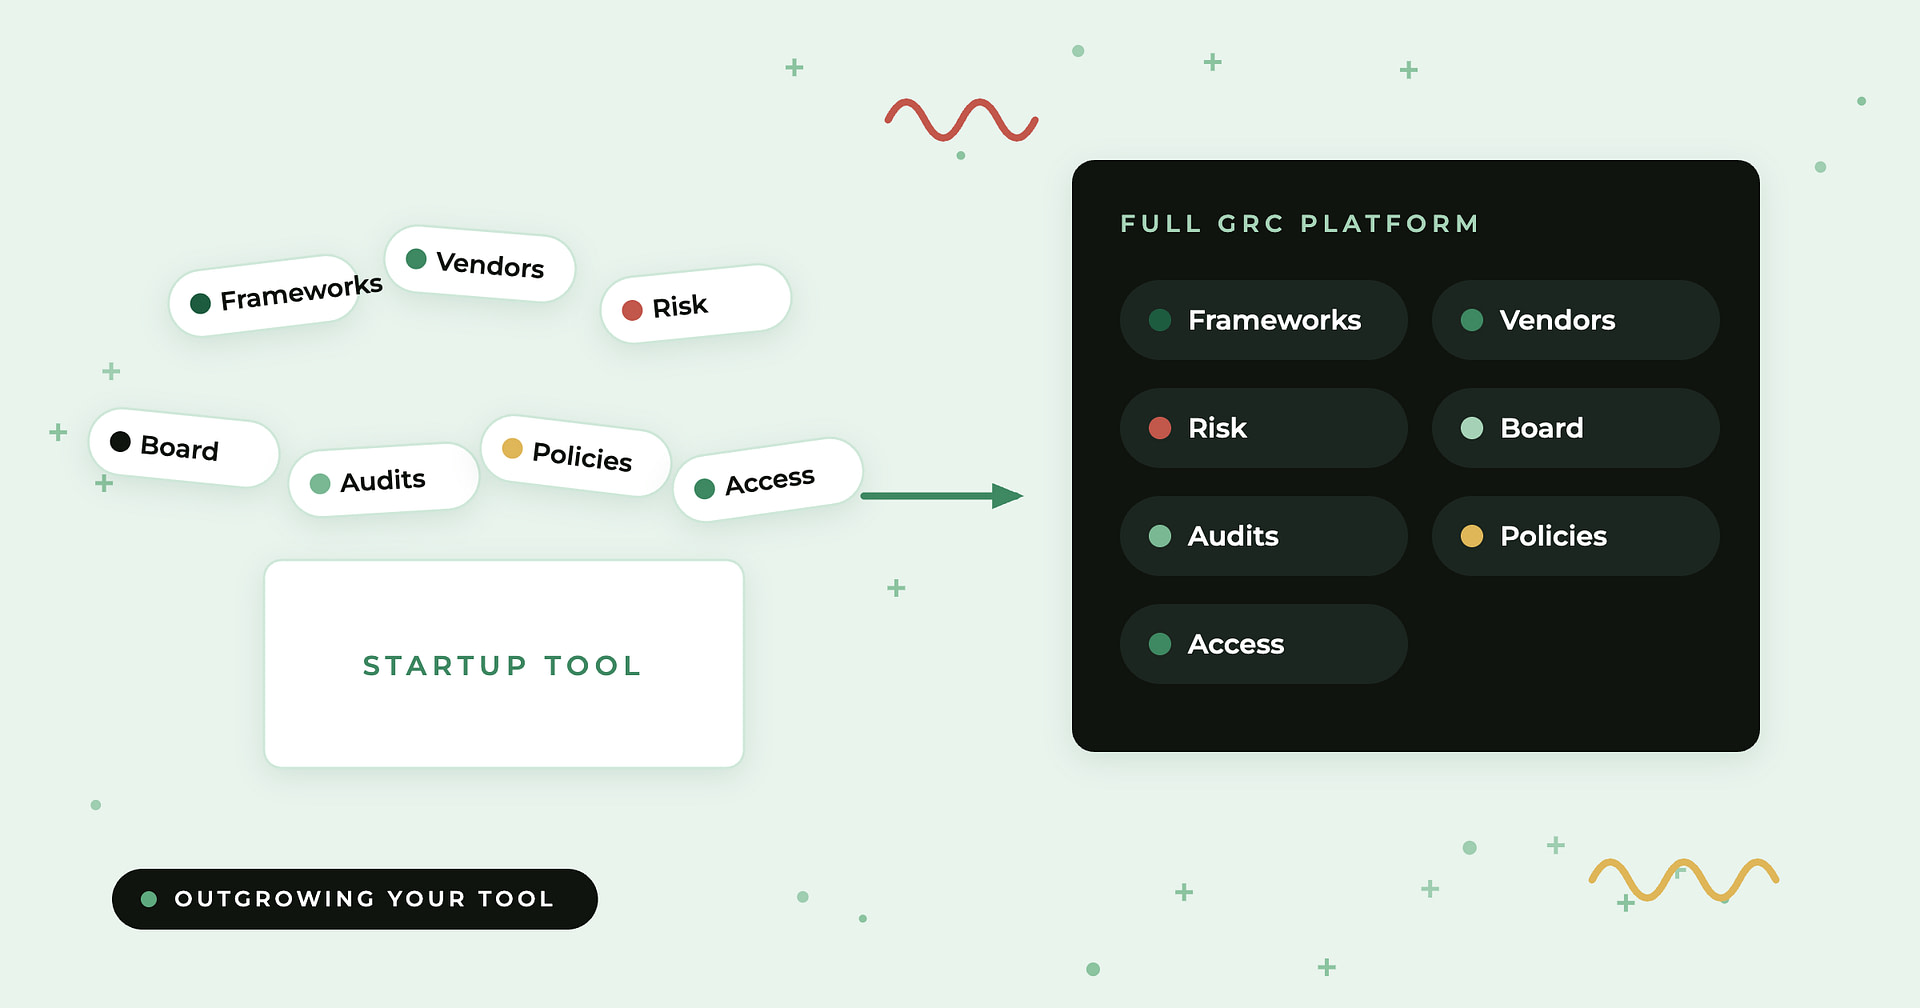
Compyl blog: Signs you have outgrown Vanta or Drata — program needs spilling out of a small startup tool into an organized GRC platform

Vanta and Drata are excellent at getting a company to its first audit. These seven signals show when a compliance program needs a full GRC platform instead.

Automated Evidence Collection for Audits: Tools and How to Choose

Compyl blog: automated evidence collection for audits — a dark hub labelled Evidence, Continuously linked by green curves to three white cards reading Collect, Map and Prove the period, above a twelve-month period tick bar on a light mint background

What evidence automation actually does, which platforms offer it, and why audits still take months at companies that own one.

Best Vendor Risk Management Software in 2026

Compyl blog: best vendor risk management software — a dark hub labelled One Vendor Register linked by green curves to three white cards reading Security ratings, Assessments and GRC platform on a light mint background

The three categories of vendor risk software, the platforms in each, how to choose, and what to ask before you buy.

Best Secureframe Alternatives in 2026 (Compared)

Compyl blog: best Secureframe alternatives — one dark control-library hub linked by green curves to four white cards labelled SOC 2, ISO 27001, HIPAA and PCI DSS on a light mint background

The best Secureframe alternatives in 2026, compared by scope and architecture — and the questions to ask every vendor before you sign.

By clicking “Accept”, you agree to the use of cookies on your device in accordance with our Privacy and Cookie policies