To redefine GRC by delivering flexible, powerful solutions that help organizations confidently manage risk and compliance with clarity and ease.
One platform for the whole GRC lifecycle, with agentic AI that removes the busywork and leaves your experts in control.

Compyl was founded in 2020 by former CISOs Stas Bojoukha and Simon Shaddock, who experienced firsthand the frustration of managing security and compliance through disconnected point solutions. Organizations were left stitching together tools just to answer a basic question.
Built by practitioners for practitioners, Compyl delivers a modern, integrated GRC platform that replaces patchwork processes with clarity, automation, and confidence — helping organizations at any stage turn GRC into a strategic advantage.

Former CISO. Built Compyl to answer the question every board asks.

Former CISO. Designed the platform around how practitioners actually work.
We build with integrity, think ahead, and stay focused on delivering real impact for the people who rely on us.
Trust is at the center of any well-functioning team. We do what we say and hold ourselves to the standard we set for our customers.
GRC moves fast. We build for where risk and compliance are going — agentic AI, continuous monitoring, and one source of truth.
We measure success by the time we give back to security teams and the confidence we put behind every decision they make.
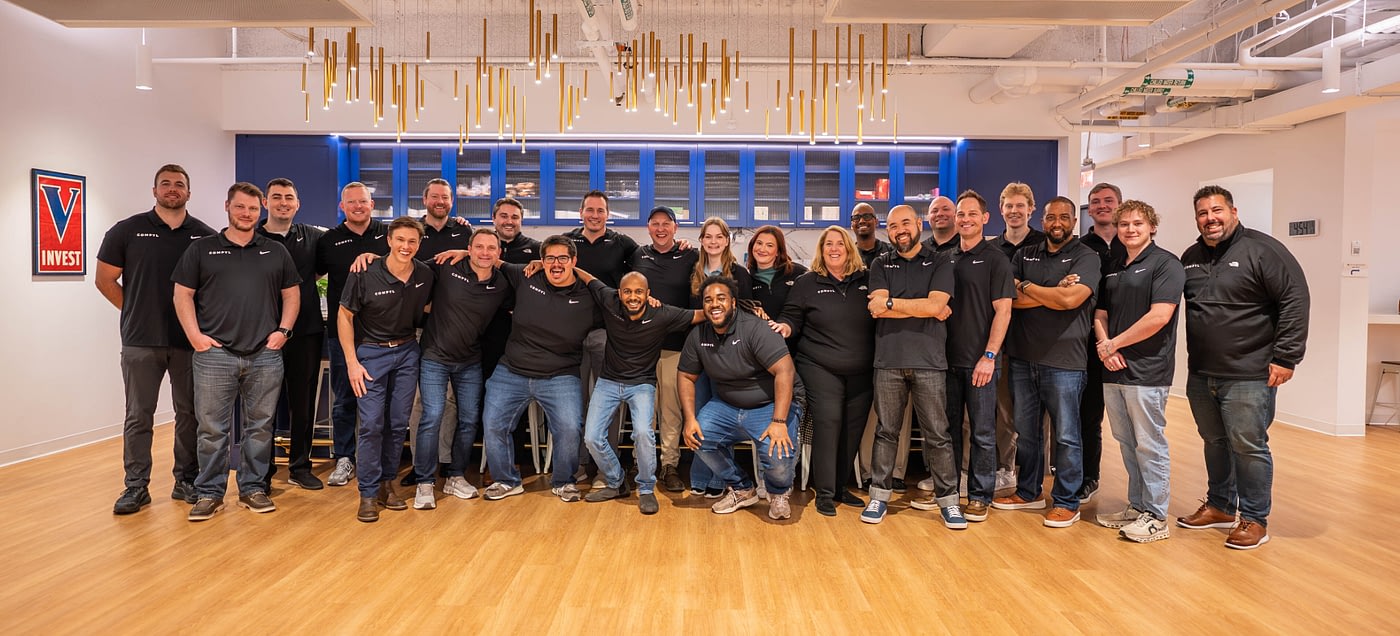
As our team continues to grow, we stay consistent with our mission and values.


Compyl is SOC 2 audited and monitored continuously on Compyl itself. Read how we secure the platform, or see what the teams who use it say on G2.
One platform for the whole GRC lifecycle, with agentic AI that removes the busywork and leaves your experts in control.