Compyl

AI

2027 Compliance Deadline Calendar: Security, Privacy & AI Dates
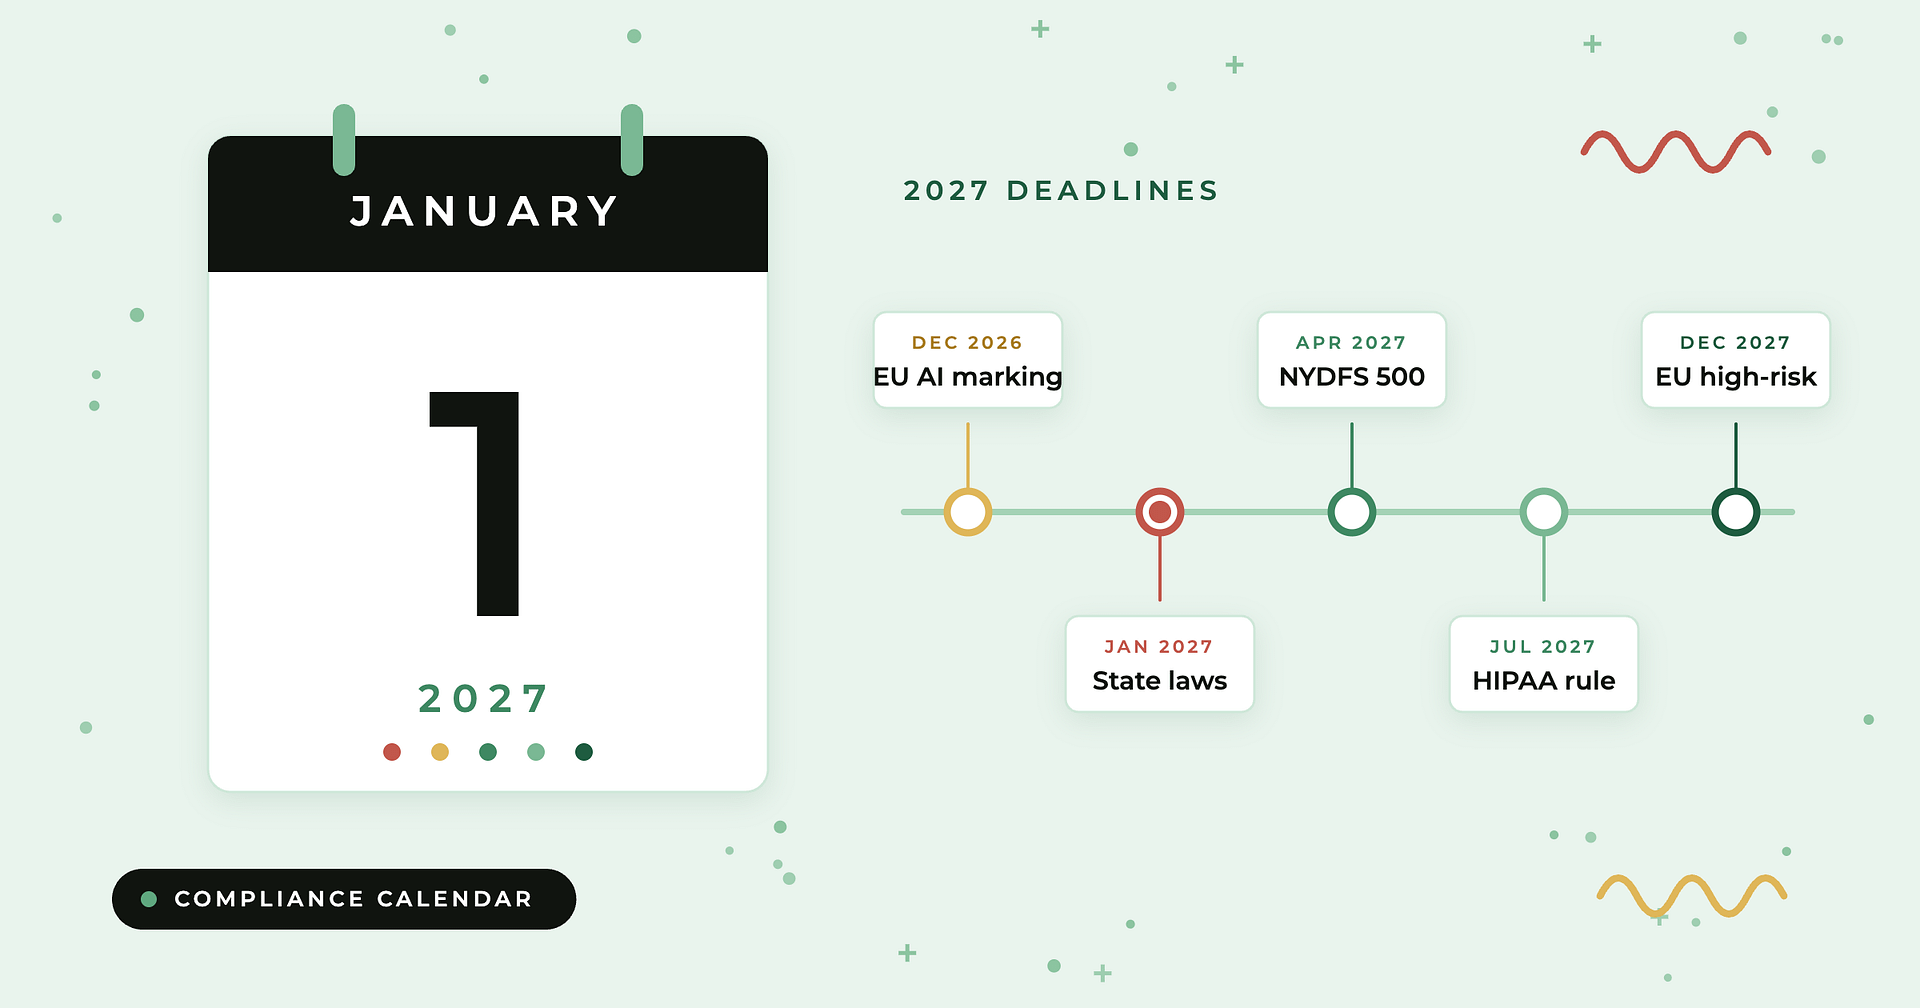
Compyl blog: 2027 compliance deadline calendar — a January 1, 2027 calendar page beside a timeline of key deadlines

A living calendar of every verified security, privacy and AI compliance deadline mid-market teams face from Q4 2026 through 2028, including the EU AI Act and HIPAA dates that moved in 2026.
The EU AI Act’s High-Risk Deadline Moved: What Actually Took Effect on August 2, 2026

The EU AI Act's High-Risk Deadline Moved: What Actually Took Effect on August 2, 2026

Regulation (EU) 2026/1744 pushed the AI Act’s high-risk obligations to December 2027 and August 2028. But Article 50 transparency rules and the AI Office’s power to fine GPAI providers went live on schedule.

What Are AI-Guided Compliance Actions? (And Which GRC Platforms Provide Them)

Compyl blog: AI-guided compliance actions — an AI spark drafts action cards that flow to a human approval check

AI-guided compliance actions are tasks an AI prepares — evidence, control mappings, questionnaire answers — that a human reviews and approves. Learn which GRC platforms deliver them.

AI Governance: The Complete Guide for 2026

AI governance guide - neural network and governance shield illustration

By Compyl Research · Last updated October 2026 AI governance is the system of policies, … AI Governance: The Complete Guide for 2026

What Is Agentic GRC? The Definitive Guide to Agentic AI in Governance, Risk & Compliance

Agentic GRC — AI-powered governance, risk and compliance

Agentic GRC explained: how AI agents automate evidence, monitoring, and risk work while humans approve every consequential decision — with use cases, comparisons, and FAQ.

Will AI Replace Compliance and GRC Teams?

Will AI replace compliance and GRC teams

Will AI replace compliance and GRC teams? No — but it is reshaping the work. What AI automates, what stays human, and how to position your team.

AI Governance Frameworks Compared: NIST AI RMF vs ISO 42001 vs EU AI Act

AI governance frameworks compared: NIST AI RMF, ISO 42001, EU AI Act

NIST AI RMF vs ISO 42001 vs EU AI Act compared: scope, force, certification, and how to use all three together. A plain-English guide.

AI Governance for Mid-Market Companies: A Practical EU AI Act Compliance Roadmap (Updated for the 2027 Deadline)

AI Governance for Mid-Market Companies: A Practical EU AI Act Compli

A 12 to 16 week roadmap to EU AI Act readiness for mid-market companies, from AI inventory to risk classification, ahead of the December 2027 high-risk deadline.

EU AI Act Compliance and GRC: What Security Teams Need to Know (Updated: Deadline Moved to December 2027)

EU AI Act Compliance and GRC: What Security Teams Need to Know Befor

Updated October 2026: The EU’s Digital Omnibus on AI (Regulation (EU) 2026/1744), in force since … EU AI Act Compliance and GRC: What Security Teams Need to Know (Updated: Deadline Moved to December 2027)

How to Evaluate AI Claims in GRC Platforms: A CISO’s Buyer Checklist for 2026

How to Evaluate AI Claims in GRC Platforms: A CISOs Buyer Checklist

How to Evaluate AI Claims in GRC Platforms: A CISO’s Buyer Checklist for 2026 TL;DR: … How to Evaluate AI Claims in GRC Platforms: A CISO’s Buyer Checklist for 2026

By clicking “Accept”, you agree to the use of cookies on your device in accordance with our Privacy and Cookie policies