Who’s on this one
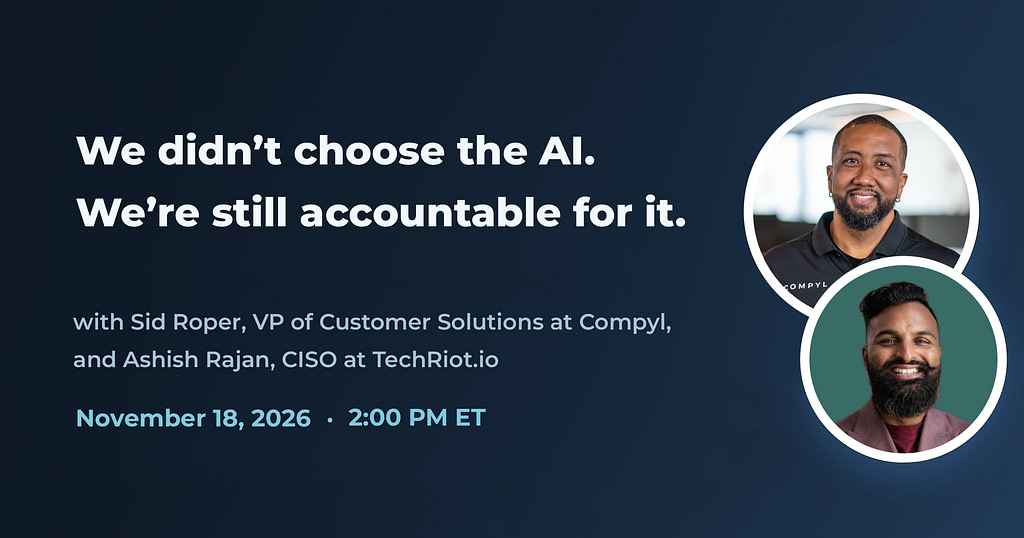
Ashish Rajan — CISO, TechRiot.io; co-host of the Cloud Security Podcast and the AI Security Podcast; author of AI Security Engineering (Wiley, 2026). His argument: AI security doesn’t fail because of tools — it fails when no one can answer who is responsible for the decision an AI system just made.
Sid Roper — VP of Customer Solutions, Compyl. 24 years in cybersecurity and GRC, spent replacing manual chaos with automated trust and scalable compliance.
Daniel Tangney — Host, GRC Radio.
Who should be in the room
- CISOs and security leaders — you inherited three or four AI dependencies this year that nobody reviewed, and the board is going to ask who owns them.
- GRC and compliance managers — ISO 42001, NIST AI RMF and the EU AI Act all expect the same first artifact, and you probably don’t have it yet.
- Vendor risk and procurement owners — the AI vendor is now a critical vendor, whether or not the contract was written that way.
Run of show
Forty-five minutes. Roughly 35 of conversation, 10 of your questions. No slides.
- The dependencies nobody chose — how every company ended up with AI in the stack before anyone reviewed it, and why “we didn’t pick it” doesn’t move the accountability.
- “Who is responsible for this decision?” — why AI security fails on ownership, not tooling, and what it looks like when nobody can answer.
- The AI inventory — the first artifact ISO 42001, NIST AI RMF and the EU AI Act all expect. What goes in it, and how to build it without a six-month project.
- An owner for every system and every agent — what “owner” has to mean when the thing can act on its own, and who signs for an agent nobody offboards.
- Your AI vendors are critical vendors — what changes in the review, the contract and the monitoring when the vendor is a model provider, or an AI feature inside a product you already bought.
- The fragmentation problem — detection, scanning, policy and monitoring bought separately, and the accountability gap that lives between them.
- Live Q&A — open floor.