How to Get Real-Time Risk and Compliance Visibility

What it takes to see risk and compliance as it is today rather than as of the last audit, and which kinds of GRC platforms deliver it.
What it takes to see risk and compliance as it is today rather than as of the last audit, and which kinds of GRC platforms deliver it.

Seven steps for managing hundreds of vendors without growing the team: tiering, automated assessments, reused evidence, continuous monitoring and one risk register.

Six steps to move a risk program from reacting to incidents and audit findings to seeing risk early and deciding in advance what to fix.

A ranked guide to risk management software for banks, credit unions and fintechs in 2026, grouped by category, with the FS regulations to check and how to move your board from heat maps to risk in dollars with FAIR.
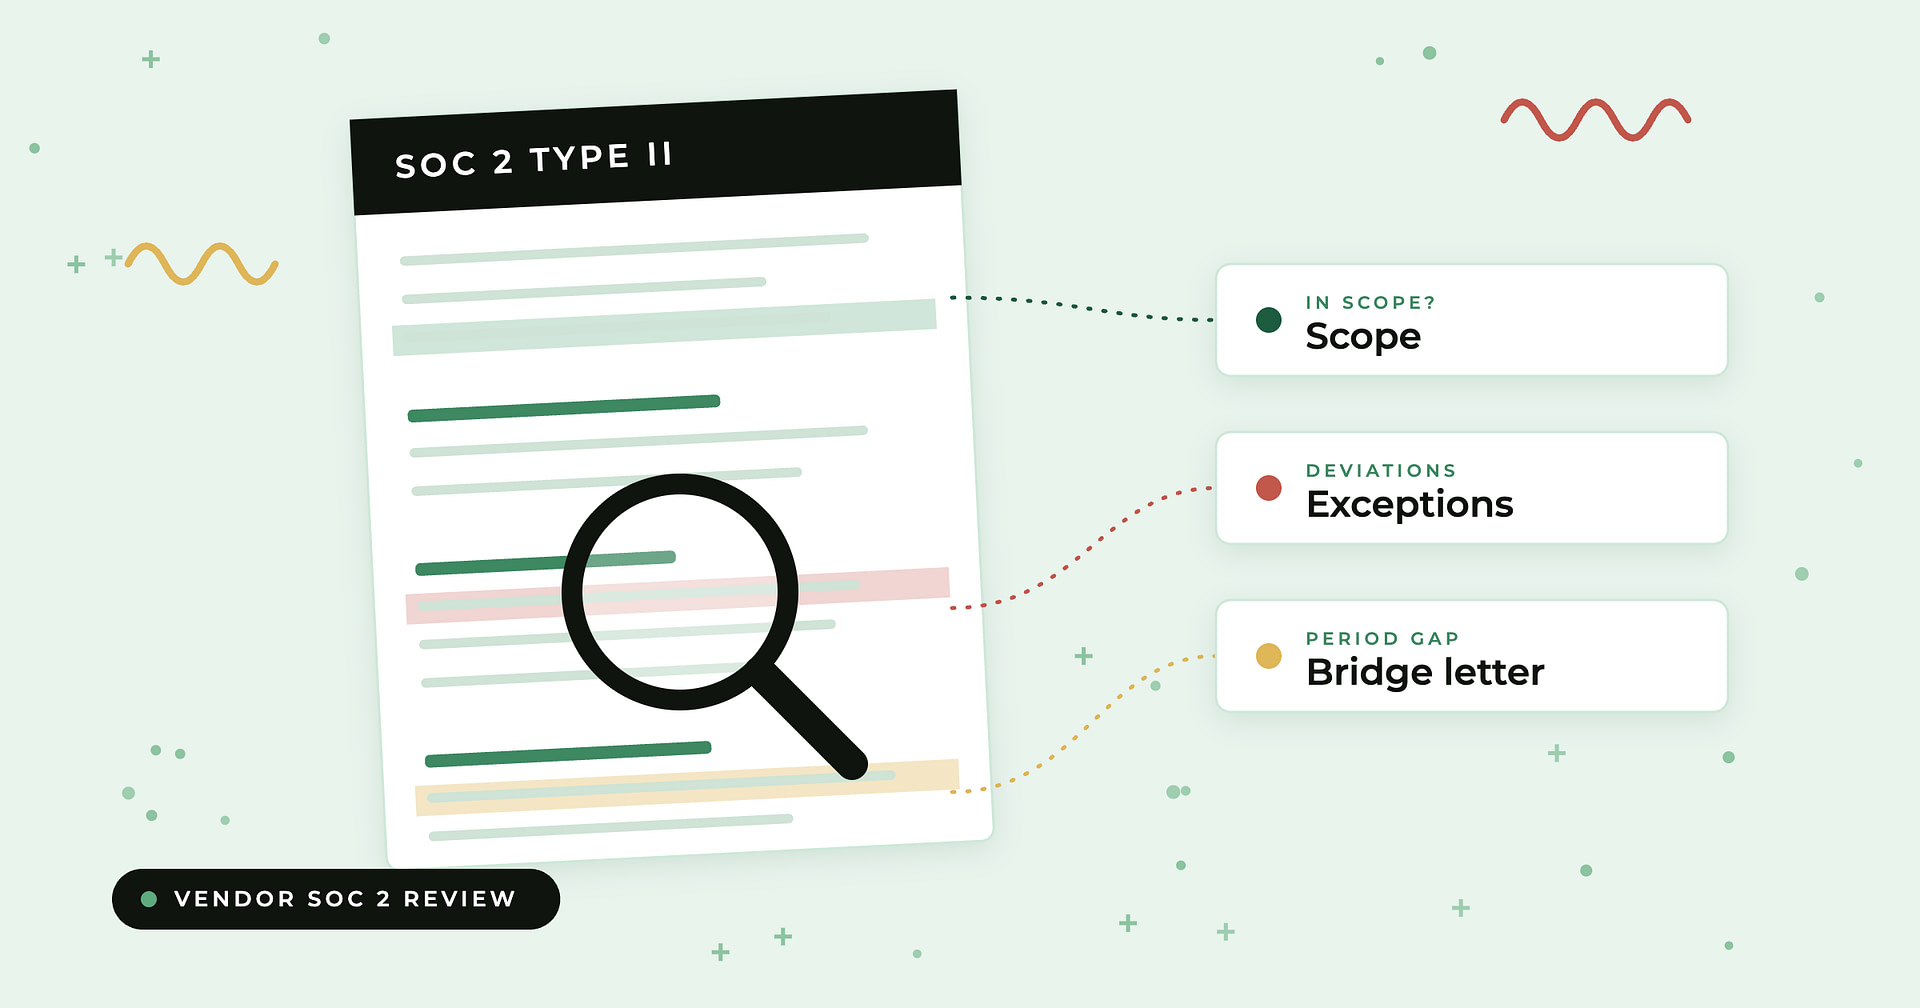
A step-by-step checklist for reviewing a vendor’s SOC 2 report, from scope and carve-outs to CUECs, exceptions, bridge letters, and the gaps SOC 2 leaves around AI and fourth parties.
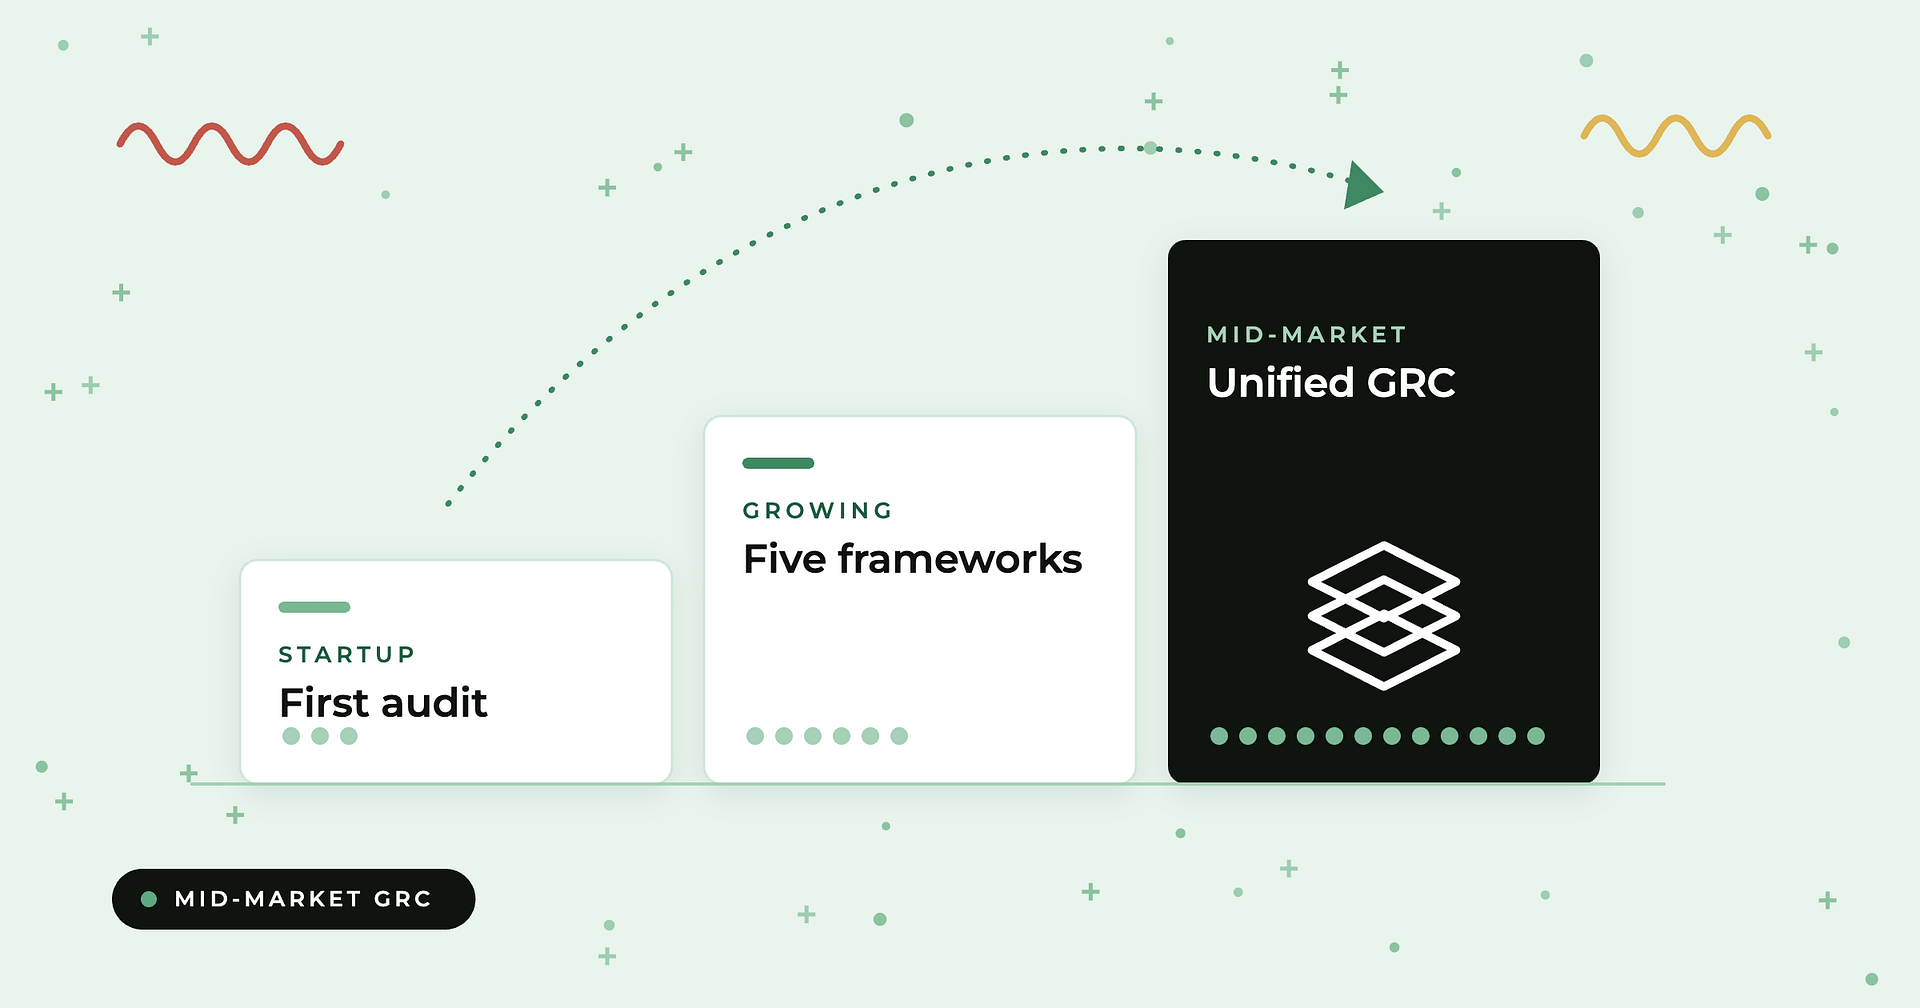
Which GRC software fits a 200–1,000-employee company depends on what is breaking first. We group the leading platforms by stage and need, with a decision table and the questions to ask before buying.
The three categories of vendor risk software, the platforms in each, how to choose, and what to ask before you buy.
FAIR risk quantification translates cyber risk into dollar figures using loss-event frequency, loss magnitude, and Monte Carlo simulation. Learn how it works and how Compyl automates it.
FAIR risk quantification explained in plain English: how the model turns cyber risk into dollars using Loss Event Frequency and Loss Magnitude.
Banks manage risk across lending, operations, technology, vendors, and regulations. When those risks are tracked … The Key Components of Enterprise Risk Management in Banking