Compyl

Compliance

Best Continuous Controls Monitoring (CCM) Tools in 2026
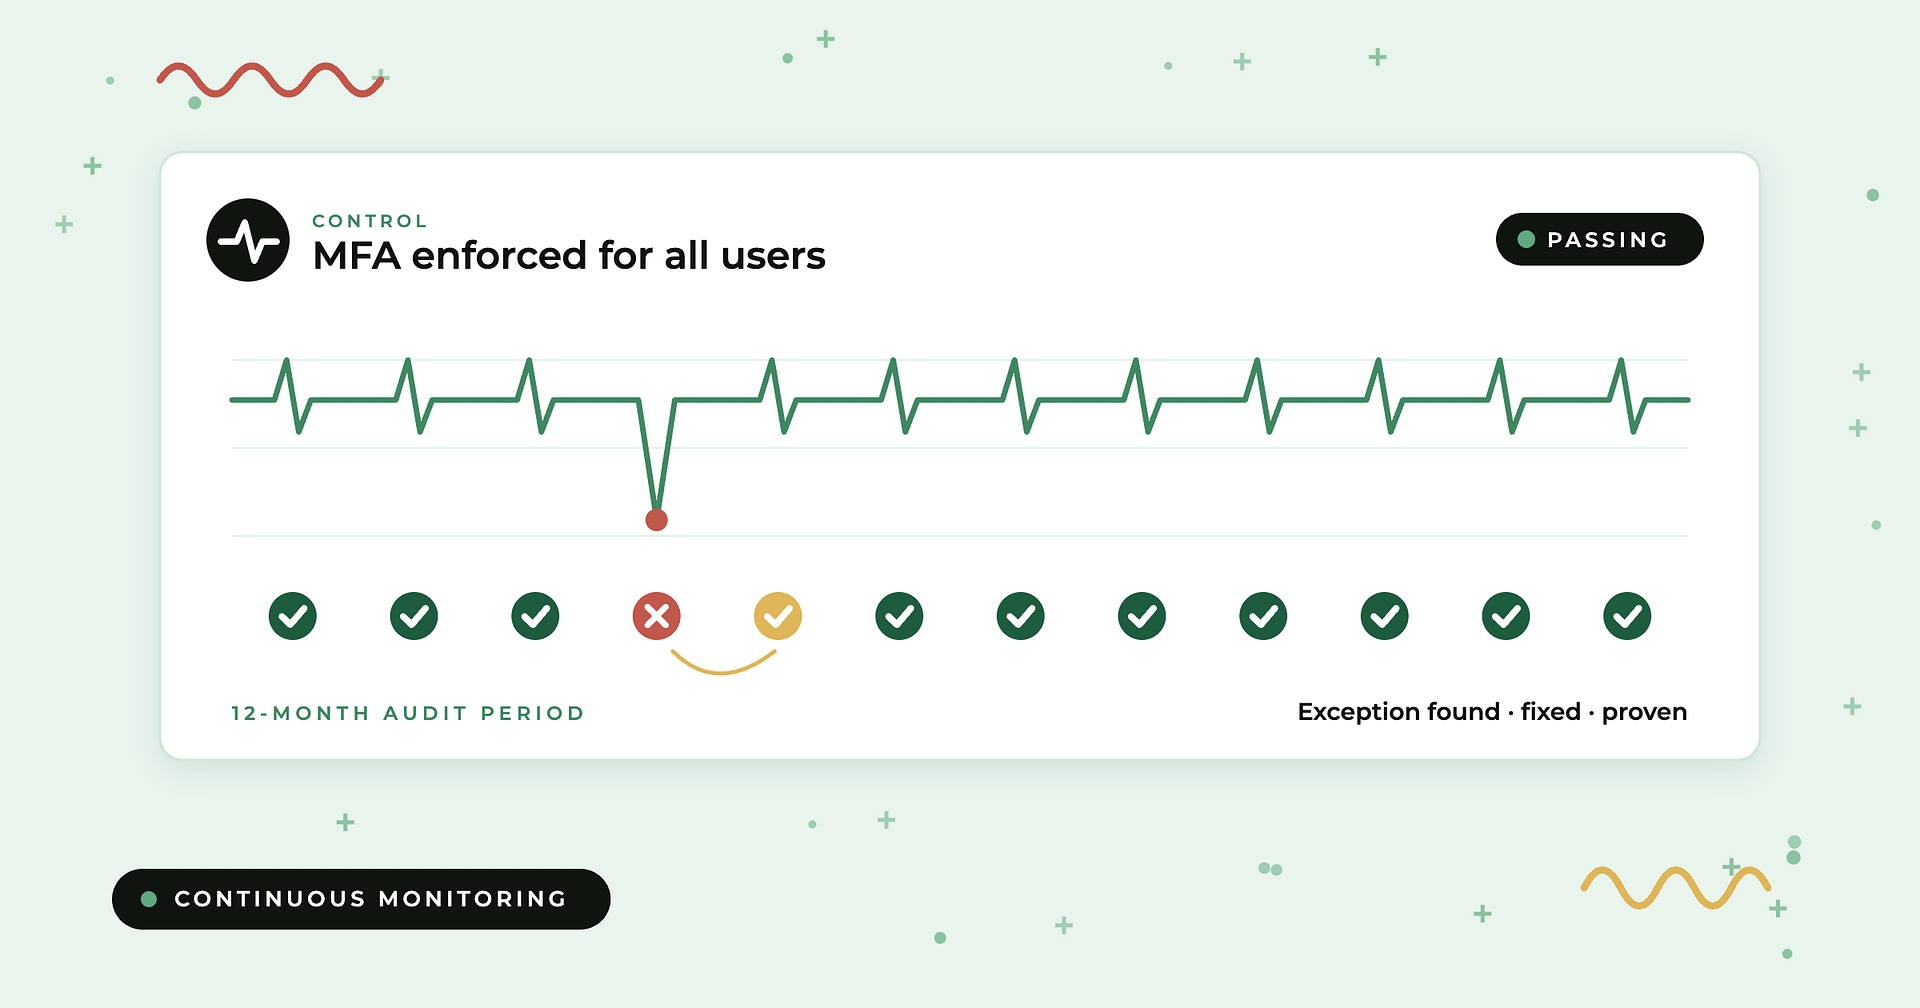
Compyl blog: Best continuous controls monitoring tools — a control monitoring panel showing a 12-month period with one exception found and fixed

The best continuous controls monitoring tools in 2026, grouped by category, and how to tell tools that monitor evidence from tools that prove controls work across the audit period.
2027 Compliance Deadline Calendar: Security, Privacy & AI Dates

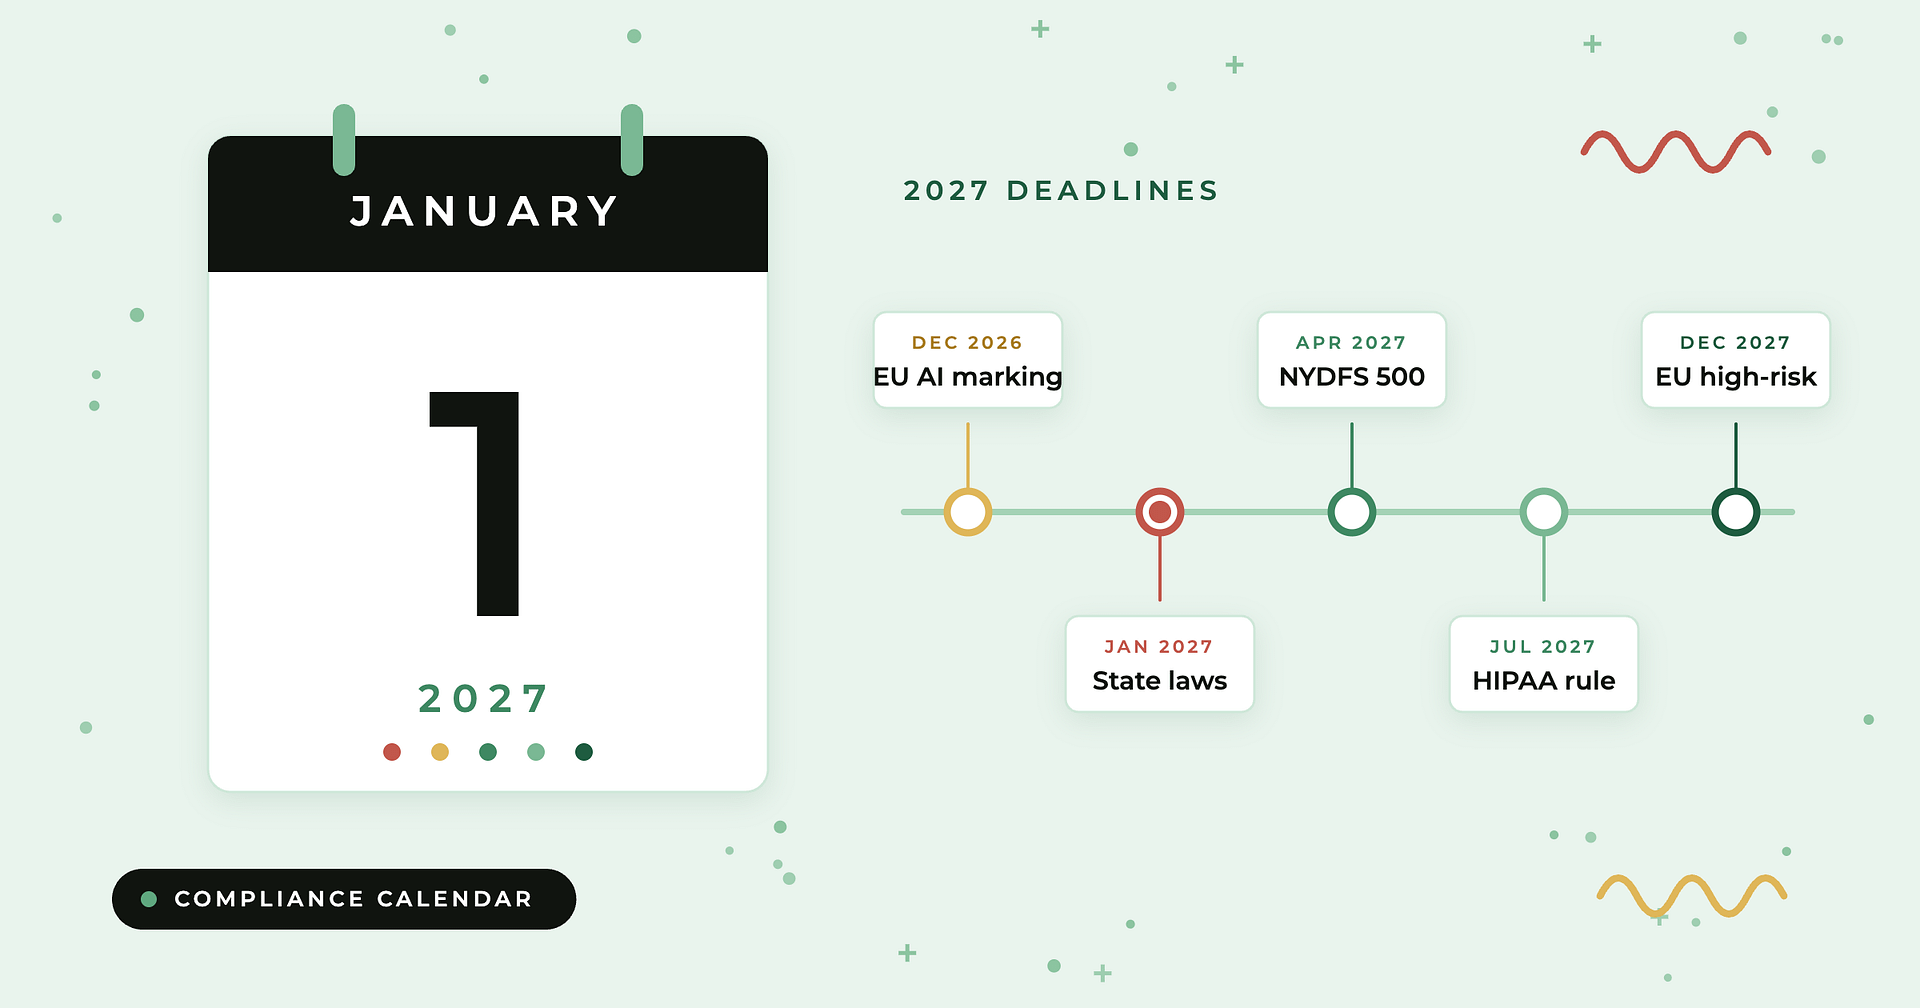
Compyl blog: 2027 compliance deadline calendar — a January 1, 2027 calendar page beside a timeline of key deadlines

A living calendar of every verified security, privacy and AI compliance deadline mid-market teams face from Q4 2026 through 2028, including the EU AI Act and HIPAA dates that moved in 2026.
How to Review a Vendor’s SOC 2 Report: What to Actually Check

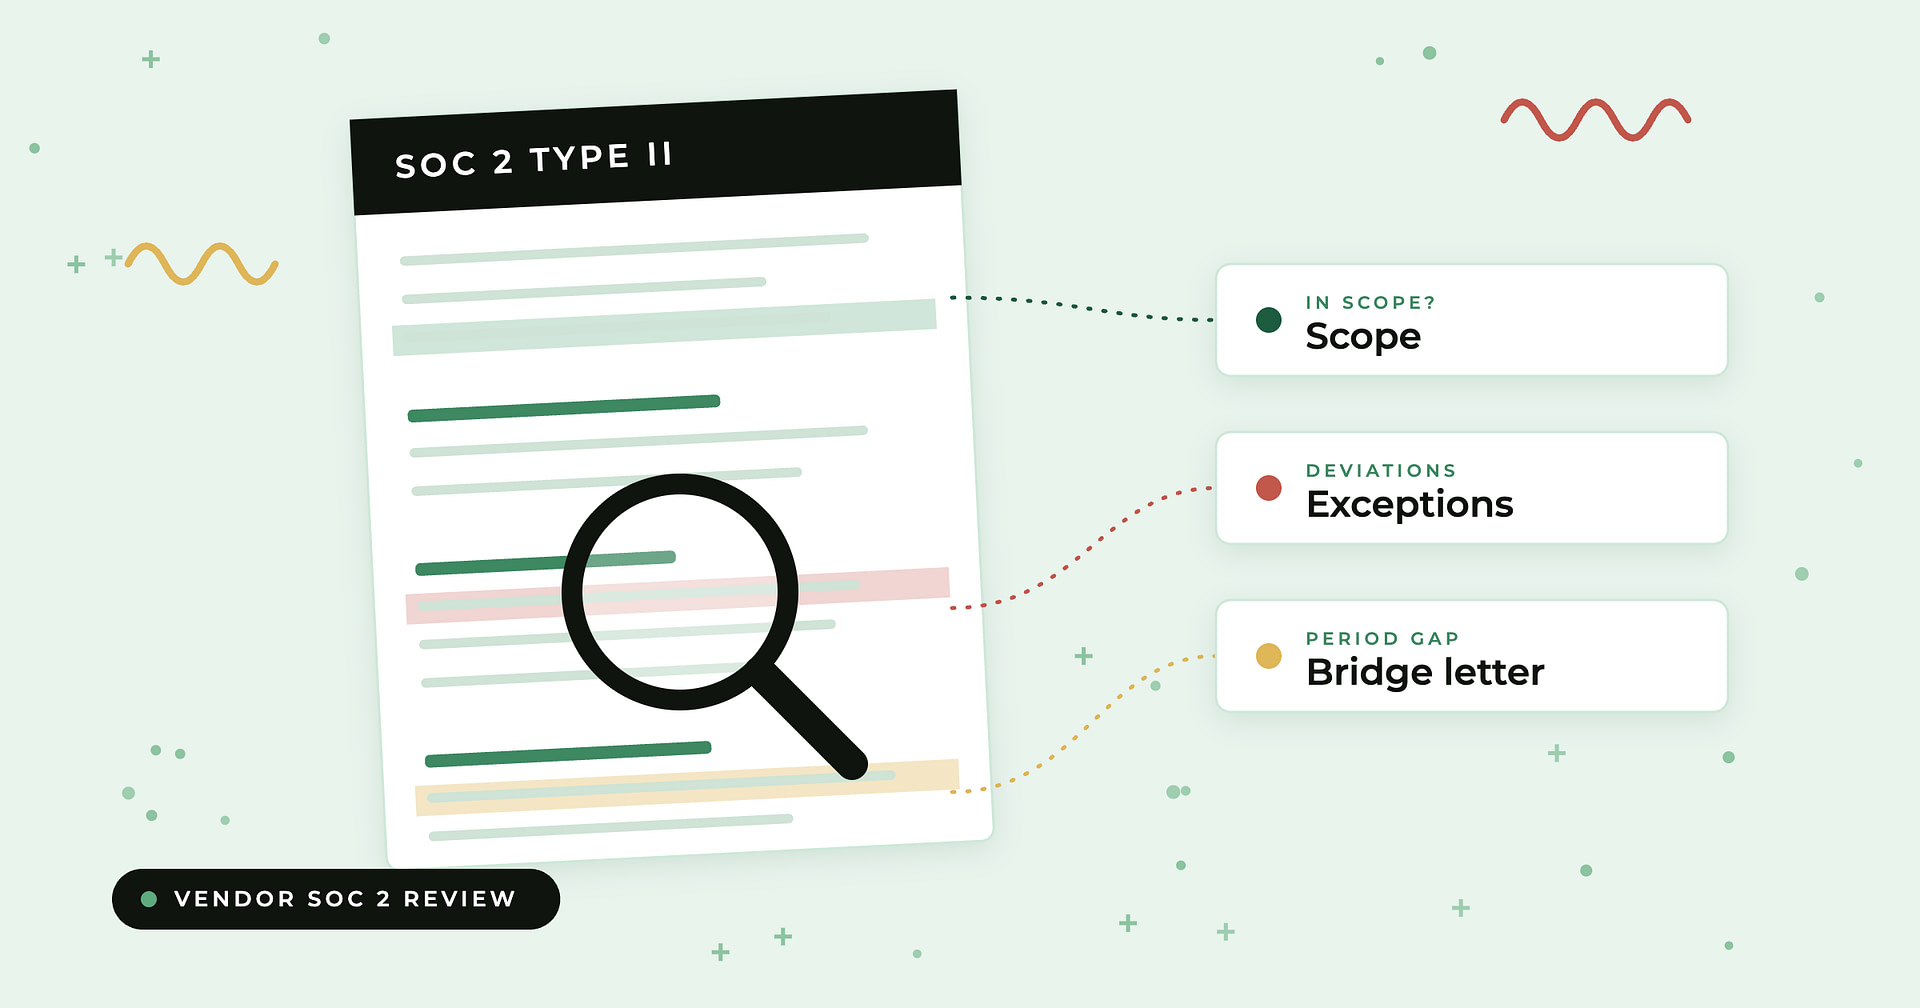
Compyl blog: How to review a vendor SOC 2 report — a magnifying glass over a SOC 2 Type II report with callouts for scope, exceptions and bridge letter

A step-by-step checklist for reviewing a vendor’s SOC 2 report, from scope and carve-outs to CUECs, exceptions, bridge letters, and the gaps SOC 2 leaves around AI and fourth parties.
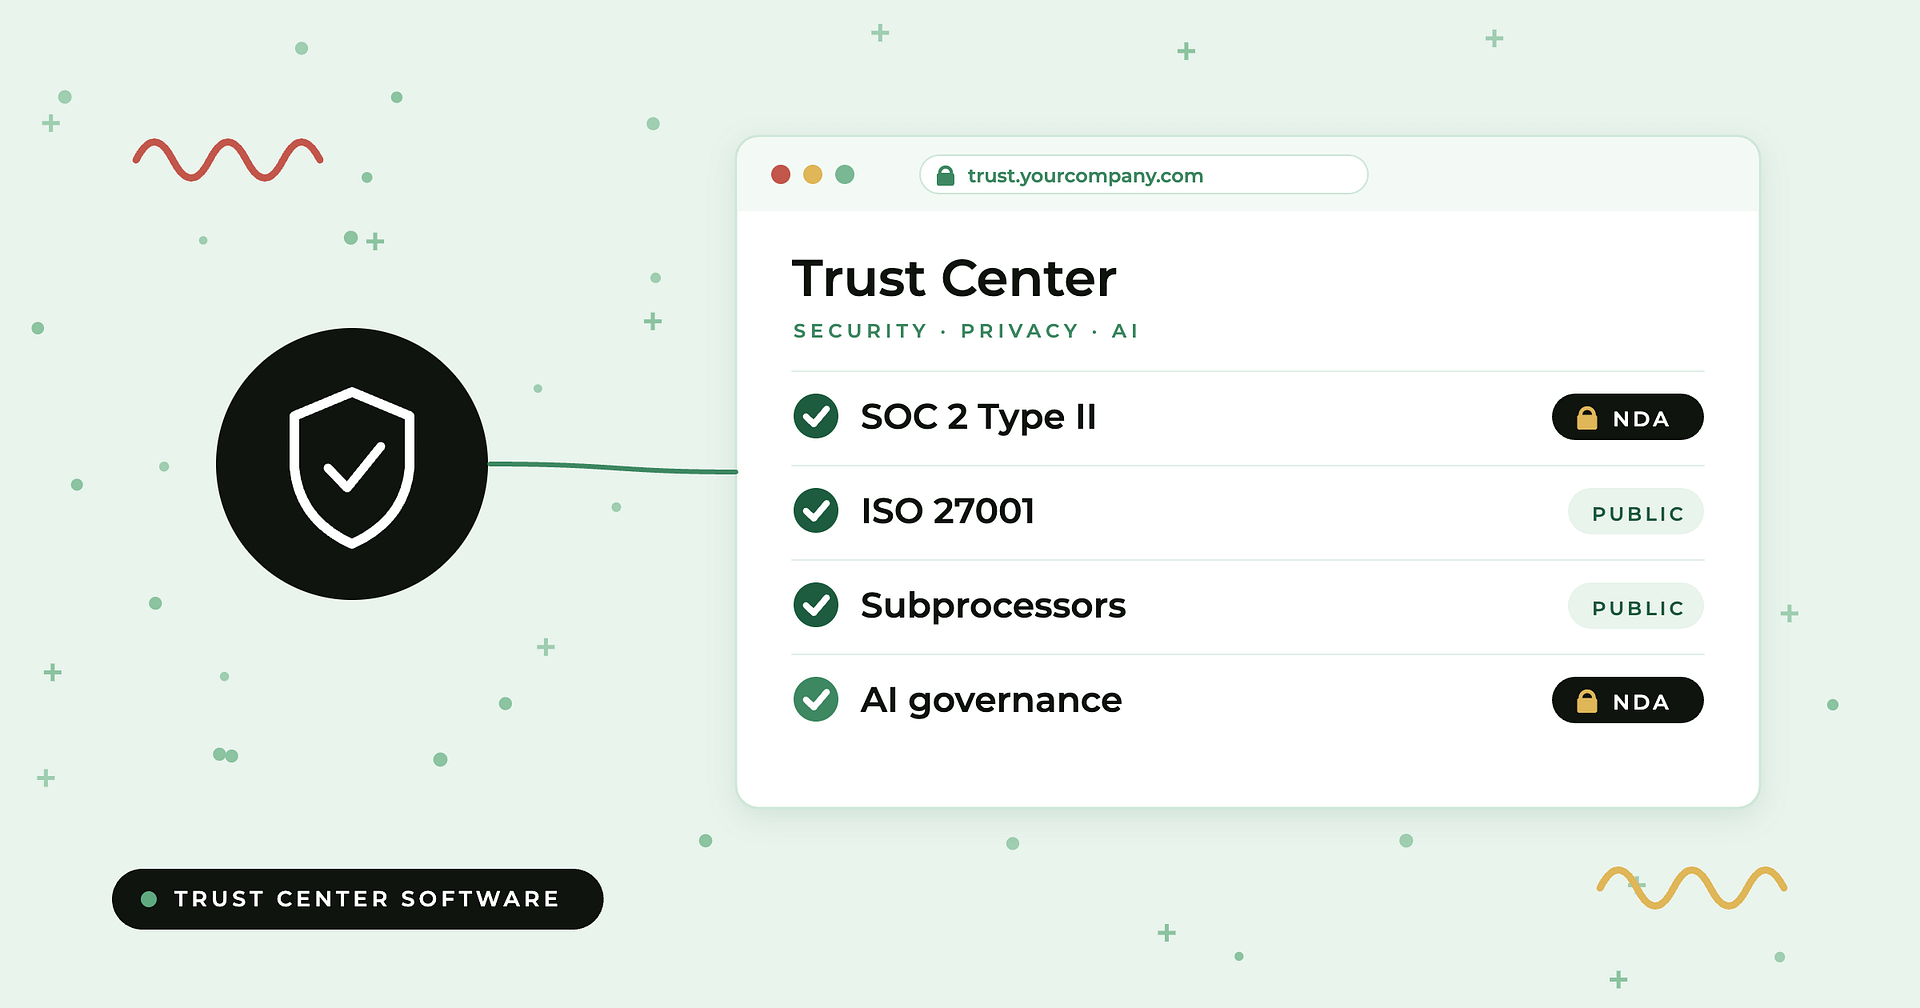
Best Trust Center Software in 2026: 11 Tools Compared

Compyl blog: Best trust center software in 2026 — a trust center portal window listing SOC 2, ISO 27001, subprocessors and AI governance with public and NDA access

The best trust center software in 2026, grouped by category: GRC platforms with a built-in trust center, compliance-automation tools, and standalone security review tools.
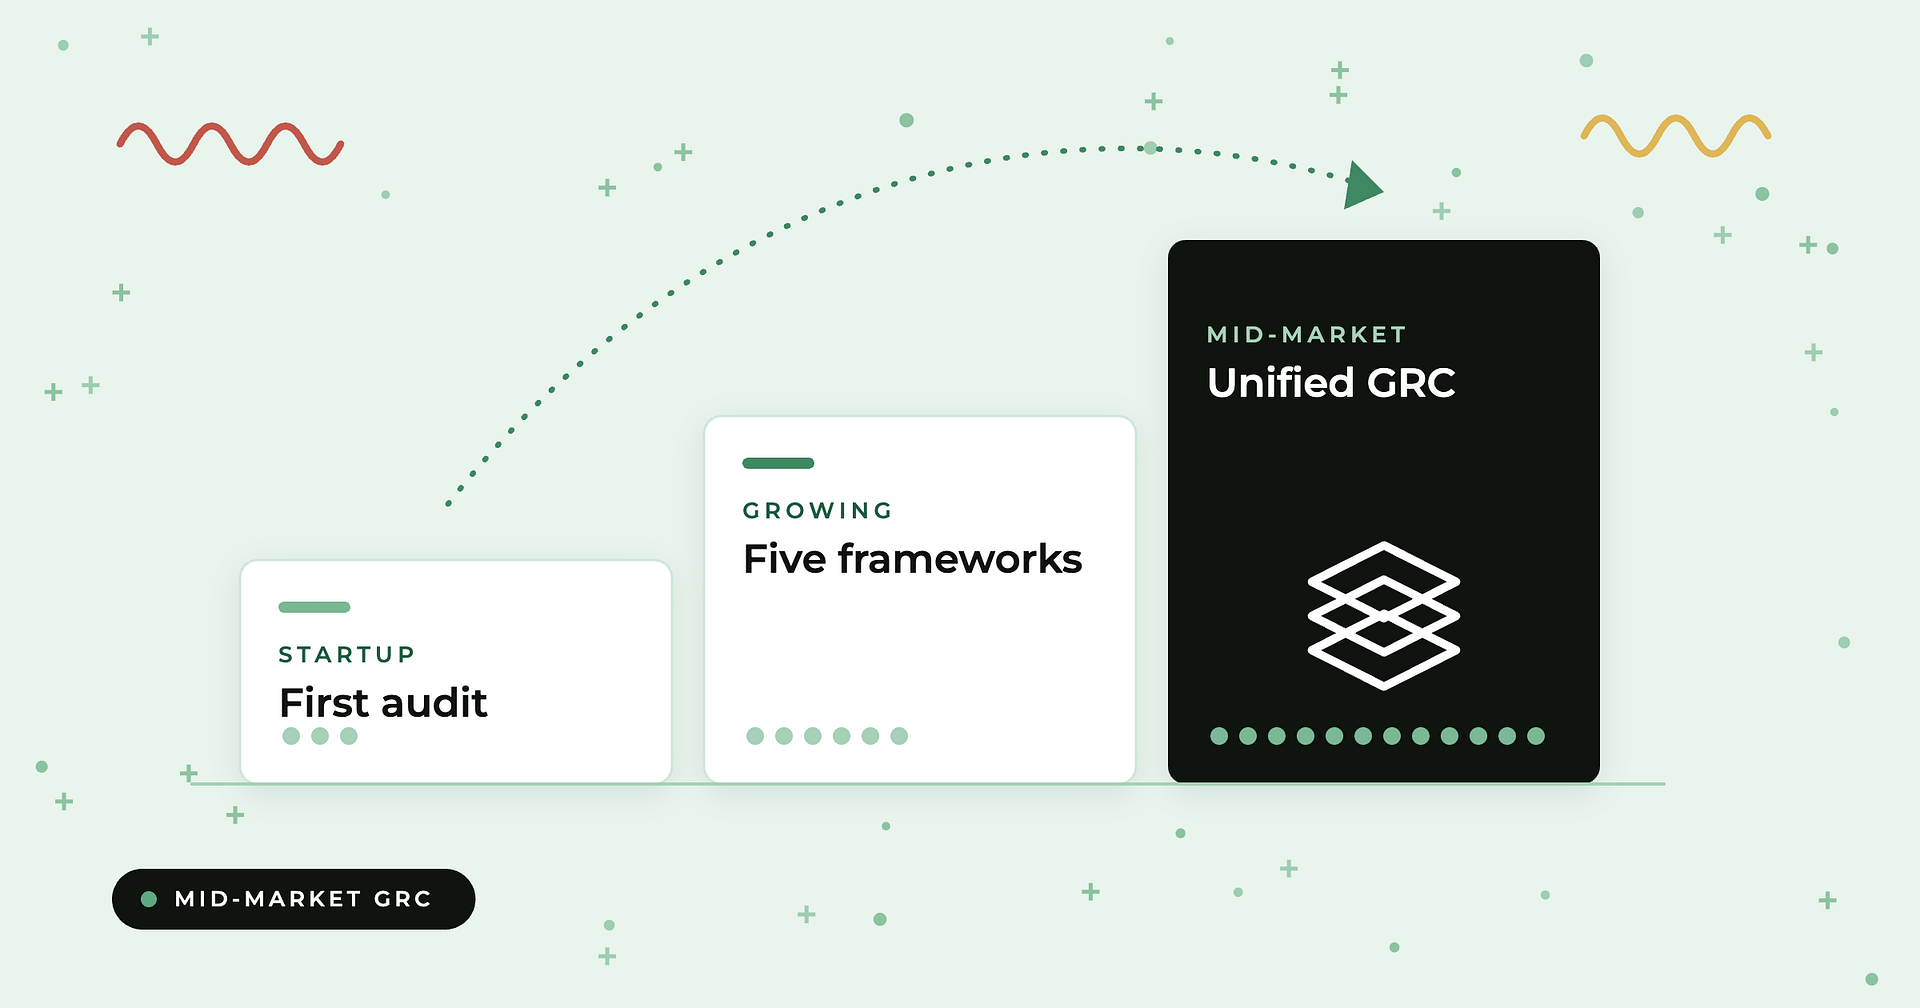
Best GRC Software for Mid-Market Companies in 2026

Compyl blog: Best GRC software for mid-market companies — three ascending stage cards from first audit to unified GRC

Which GRC software fits a 200–1,000-employee company depends on what is breaking first. We group the leading platforms by stage and need, with a decision table and the questions to ask before buying.
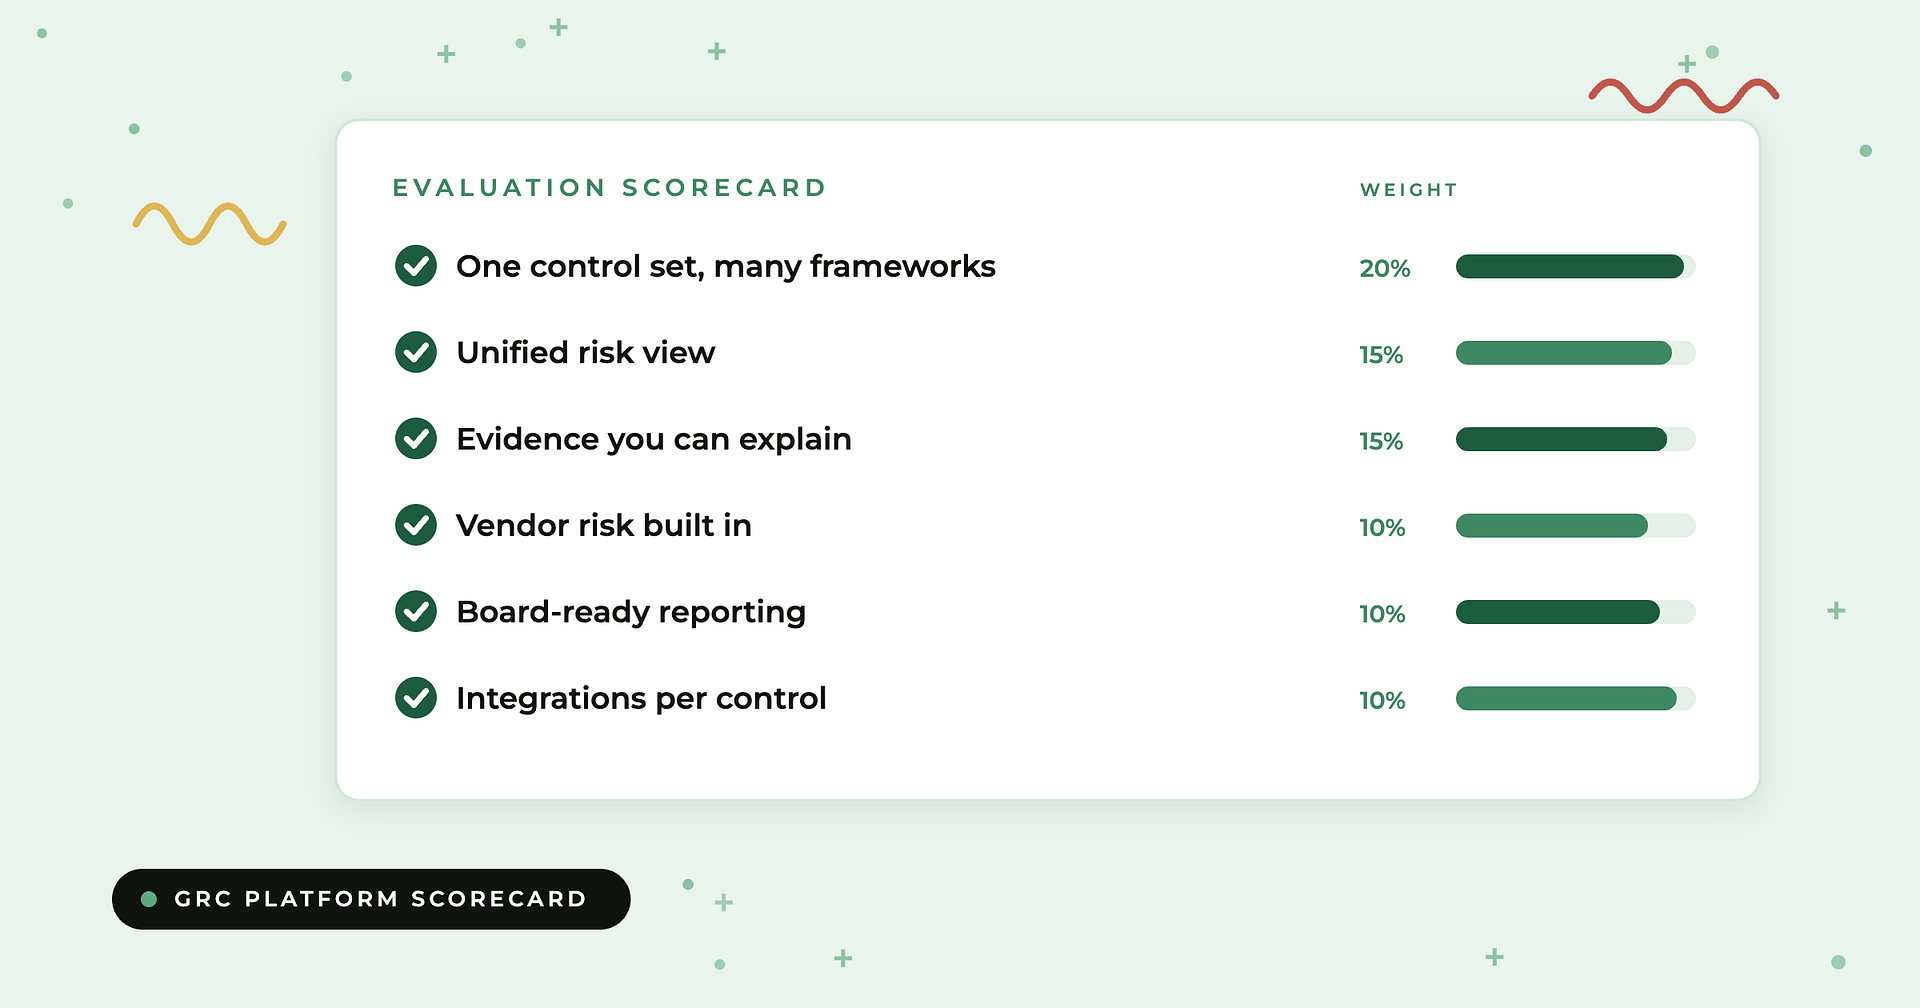
How to Evaluate an Integrated GRC Platform for Multi-Framework Compliance and a Unified Risk View

Compyl blog: How to evaluate an integrated GRC platform — a weighted evaluation scorecard of six criteria

A buyer’s guide for mid-sized and enterprise teams: the eight criteria that separate an integrated GRC platform from a compliance tool, a weighted scorecard, and the questions to ask vendors.
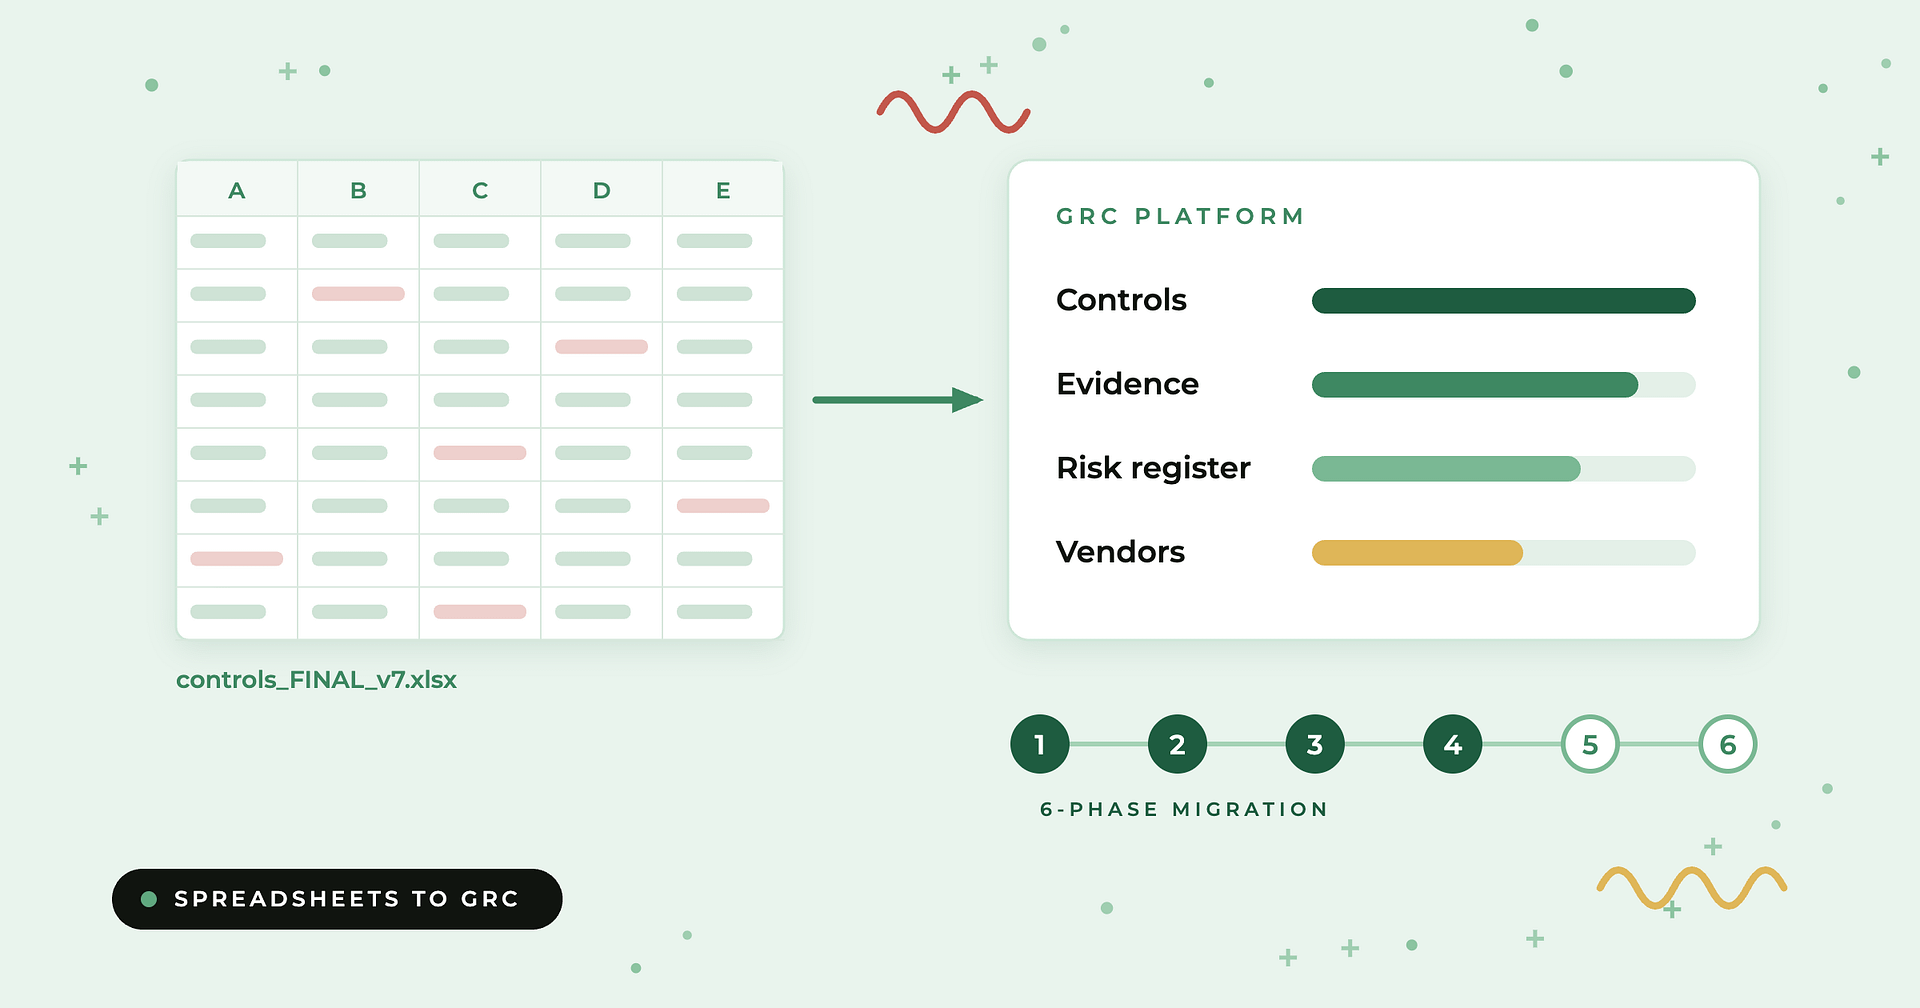
How to Replace Compliance Spreadsheets with a GRC Platform: A Phased Migration Plan

Compyl blog: Replace compliance spreadsheets with a GRC platform — a spreadsheet becoming a GRC platform view with a six-phase migration track

A six-phase plan for mid-market and enterprise teams moving their controls, evidence, risk register and vendor tracking out of spreadsheets and into an automated GRC platform.
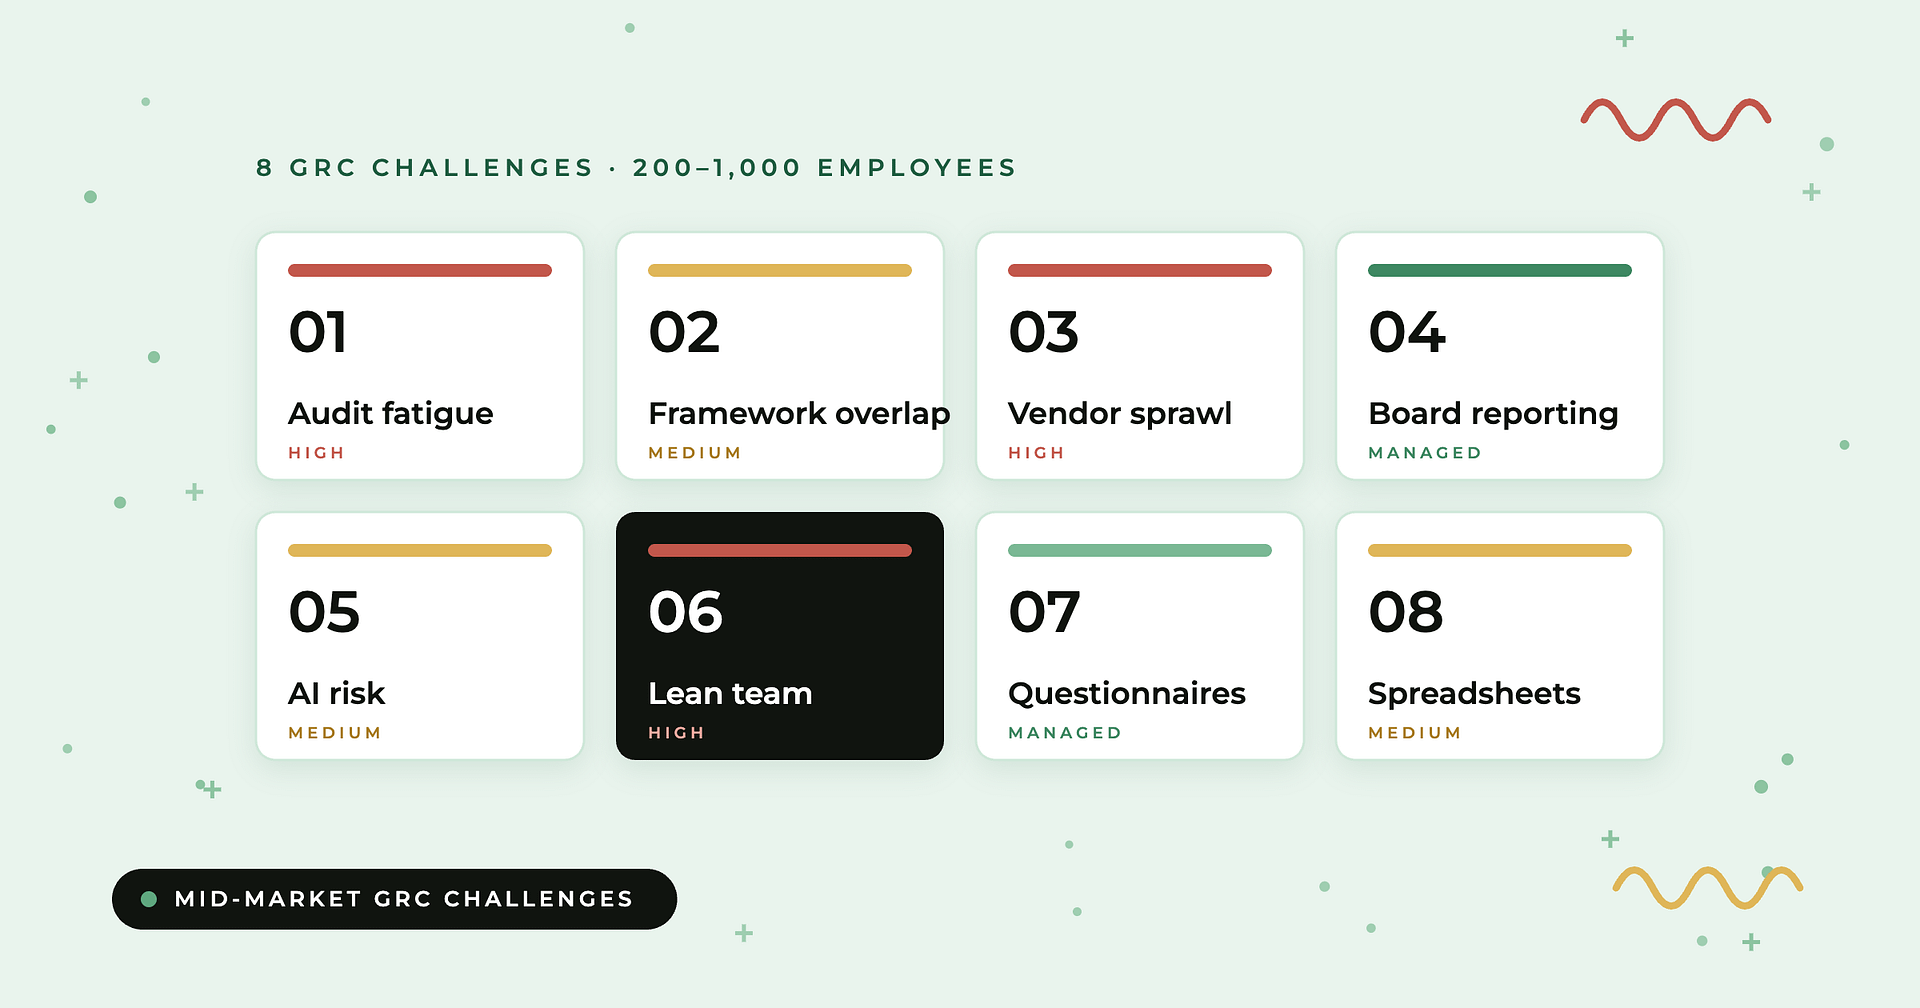
GRC Challenges Mid-Market Technology Companies Face in 2026 (and How to Solve Them)

Compyl blog: GRC challenges for mid-market technology companies — eight numbered challenge tiles rated by severity

The eight governance, risk and compliance problems that hit technology companies between 200 and 1,000 employees, and what the teams that solve them do differently.
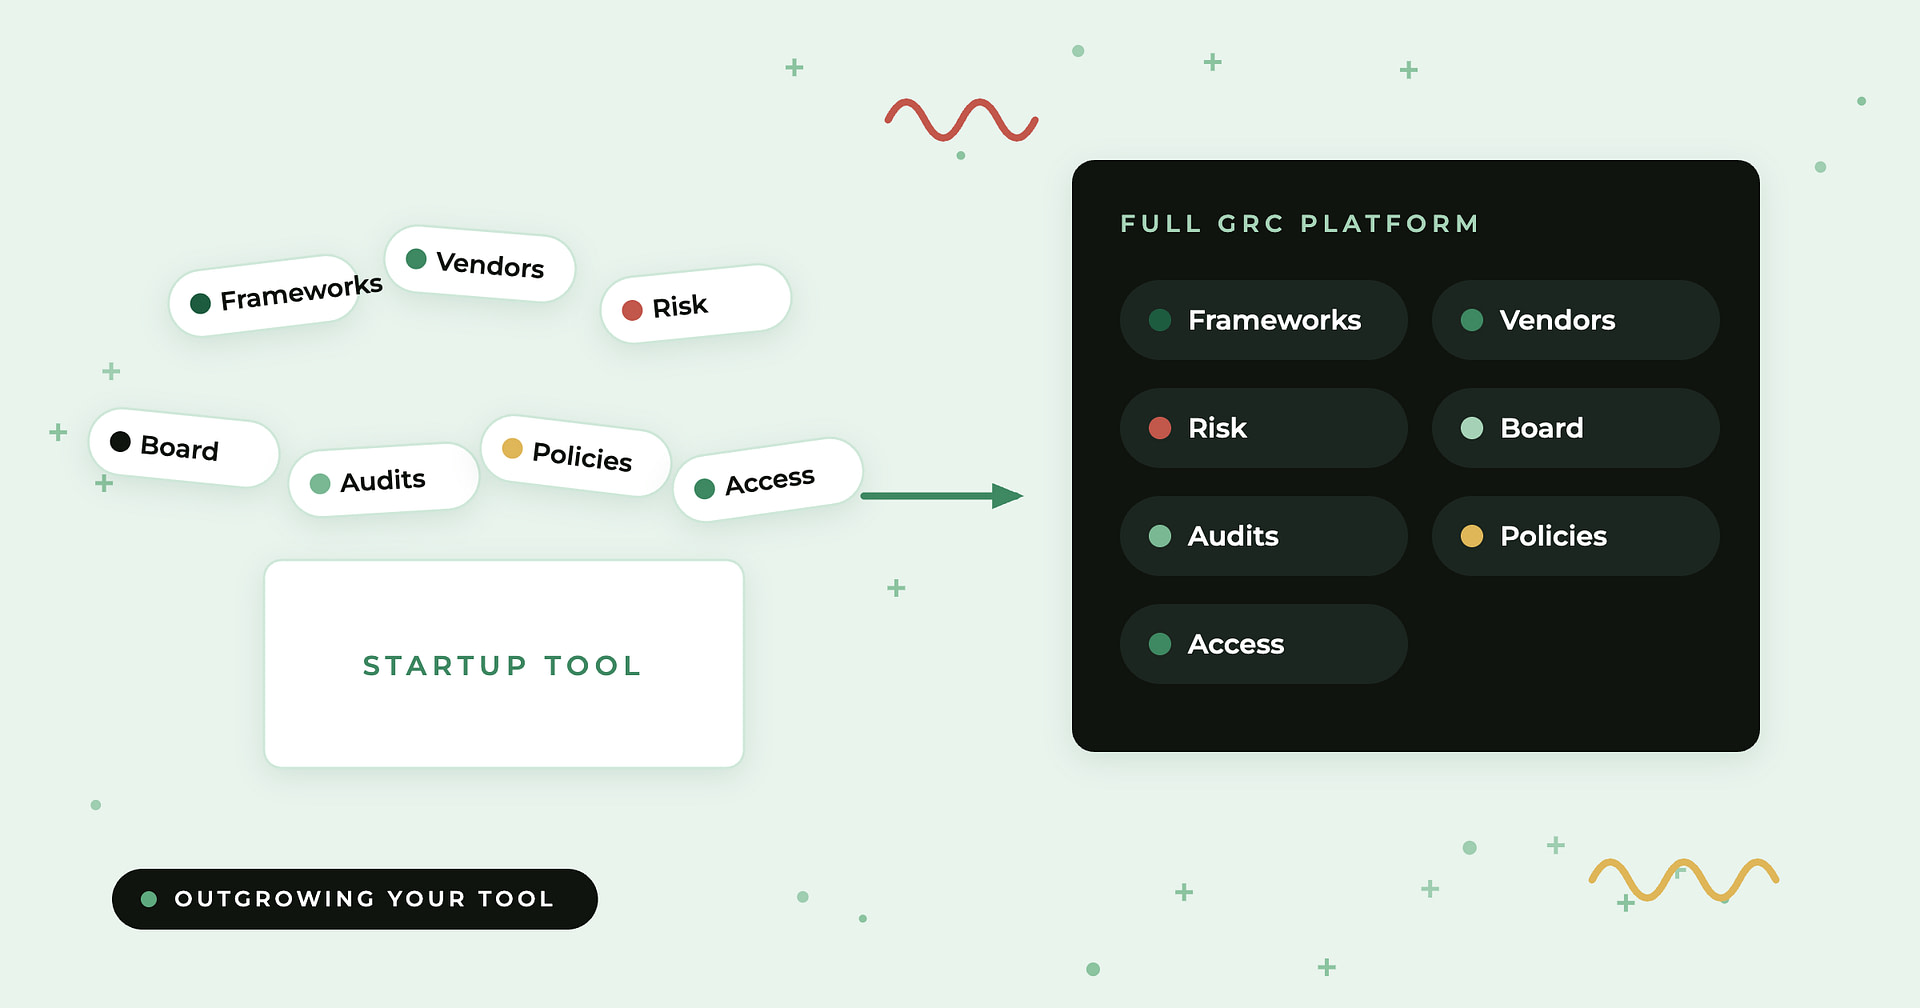
7 Signs You’ve Outgrown Vanta or Drata (and What to Move To)

Compyl blog: Signs you have outgrown Vanta or Drata — program needs spilling out of a small startup tool into an organized GRC platform

Vanta and Drata are excellent at getting a company to its first audit. These seven signals show when a compliance program needs a full GRC platform instead.

Automated Evidence Collection for Audits: Tools and How to Choose

Compyl blog: automated evidence collection for audits — a dark hub labelled Evidence, Continuously linked by green curves to three white cards reading Collect, Map and Prove the period, above a twelve-month period tick bar on a light mint background

What evidence automation actually does, which platforms offer it, and why audits still take months at companies that own one.
By clicking “Accept”, you agree to the use of cookies on your device in accordance with our Privacy and Cookie policies